The Zero-Cost WordPress Security Checklist for Small Businesses

Most small business owners think hackers are only interested in large companies with valuable customer data or deep pockets. That’s exactly what makes smaller websites easy targets.

Cyberattacks today aren’t personal. They’re automated. Bots scan thousands of WordPress websites every hour, looking for outdated plugins, weak passwords, exposed login pages, and other common vulnerabilities.

Imagine waking up to discover your homepage redirects visitors to a gambling website, Google has marked your site as unsafe, and your customers can no longer trust your business. It happens far more often than most business owners realize, and recovering can take weeks while damaging your rankings, reputation, and customer trust.

The good news is that WordPress security for small businesses doesn’t have to be expensive. In fact, most of the protection your website needs is completely free.

This free WordPress security checklist shows you how to secure your WordPress website for free using trusted plugins, built-in WordPress settings, and simple best practices. No coding. No premium software. Just practical steps that every small business owner can implement today.

Why Are Small Businesses Vulnerable to Cyberattacks?

Most cyberattacks don’t begin with someone choosing a specific business to target. They begin with automated bots scanning thousands of WordPress websites for common weaknesses.

Before diving into the free WordPress security checklist, it’s important to understand why WordPress security for small businesses deserves immediate attention.

The Dangerous Myth That Small Sites Are Safe

Many business owners believe hackers only pursue high-profile companies. In reality, automated bots scan millions of WordPress websites every day, searching for weak passwords, outdated plugins, vulnerable themes, and exposed login pages. They don’t evaluate business size.

What a Hack Actually Does to a Small Business

A compromised WordPress website can do far more than display unwanted content. Attackers may steal customer information, inject malware, redirect visitors to fraudulent websites, or trigger Google’s security warnings that remove your pages from search results. Even a single outdated plugin has cost small businesses thousands in recovery expenses, lost revenue, and damaged customer trust.

The Good News: Free Security Covers Most Small Business Needs

The encouraging part is that effective security doesn’t have to be expensive. Regular updates, strong passwords, free WordPress security plugins, free WordPress malware protection, and free WordPress two-factor authentication stop the majority of common attacks. Spend one afternoon implementing the right measures, and your website instantly becomes far more difficult for automated bots to compromise.
No Free Security

The Complete Zero-Cost WordPress Security Checklist

A secure website isn’t built with one tool. It’s built through small, consistent improvements. Complete the following free WordPress security checklist to strengthen WordPress security for small businesses using trusted free tools and settings that take only minutes to configure.

1. Keep WordPress, Themes & Plugins Updated

Every WordPress update strengthens your website against newly discovered vulnerabilities. Keeping your core files, themes, and plugins updated reduces the chances of malware infections, unauthorized access, and compatibility issues. It’s one of the easiest yet most effective ways to improve WordPress security for small businesses without spending anything.

Why It’s Necessary

  • Closes known security vulnerabilities before hackers exploit them.
  • Protects your website from malware and automated attacks.
  • Improves plugin compatibility and website stability.
  • Keeping your website optimized also improves performance. Our WordPress Speed Optimization Services help businesses maintain both security and loading speed.

In Verizon’s 2024 Data Breach Investigations Report, 14% of data breaches involved the exploitation of vulnerabilities as the initial access method, nearly three times higher than the previous year. Hackers don’t need sophisticated techniques if websites aren’t patched. That’s exactly why updating WordPress, plugins, and themes every week should be your first security habit.

2. Install Wordfence Free: One of the Best Free Security Plugins

A good security plugin acts like a gatekeeper for your website. Wordfence provides WordPress malware protection for free, a free WordPress firewall, login monitoring, and WordPress brute force protection, making it one of the most comprehensive free security solutions available.

Why It’s Necessary

  • Blocks suspicious traffic before it reaches your website.
  • Scans files for malware and security issues.
  • Limits repeated login attempts from bots.
  • Combines multiple security features into one plugin.
  • Reduces plugin conflicts by replacing several separate security tools.

3. Enable Two-Factor Authentication on Every Admin Account

Passwords can be guessed, leaked, or stolen, but two-factor authentication adds another layer of protection. Even if someone knows your password, WordPress two-factor authentication free prevents unauthorized access by requiring a second verification step.

Why It’s Necessary

  • Protects administrator and editor accounts.
  • Prevents unauthorized dashboard access.
  • Reduces risks from stolen passwords.
  • Adds security without affecting everyday usability.

According to Verizon’s 2024 DBIR, 68% of breaches involved a human element, including stolen credentials, phishing, or user errors. Technology alone can’t secure a website. Strong passwords, two-factor authentication, and good security habits often make a bigger difference than expensive software.

4. Change the Default WordPress Login URL

The default WordPress login page is one of the first places automated bots try to access. Changing it to a custom URL adds another layer of WordPress login protection, free, making your website a far less obvious target for brute force attacks.

Why It’s Necessary

  • Reduces automated login attempts targeting /wp-admin.
  • Makes your login page harder for bots to discover.
  • Adds an extra security layer without affecting legitimate users.
  • Prevents unnecessary server load caused by repeated login requests.

5. Use Strong Passwords and a Free Password Manager

Even the best security setup can fail because of a weak password. Long, unique passwords generated with tools like Bitwarden or WordPress’s built-in password generator dramatically reduce the risk of unauthorized access while making account management much easier.

Why It’s Necessary

  • Prevents attackers from guessing or cracking passwords.
  • Reduces the risk of credential reuse across multiple websites.
  • Stores complex passwords securely in one place.
  • Makes password management simple without sacrificing security.
  • Protects every user account, not just administrators.

6. Set Up SSL and Force HTTPS

An SSL certificate protects the data exchanged between your website and its visitors by encrypting every connection. Most hosting providers offer free SSL certificate through Let’s Encrypt, allowing you to improve security and build visitor trust in just a few minutes.

Why It’s Necessary

  • Encrypts sensitive information during transmission.
  • Displays the secure padlock icon in modern browsers.
  • Prevents data interception on public networks.
  • Supports better user trust and browsing confidence.
  • Meets Google’s recommendation for secure websites.

7. Set Up Automated Backups to Google Drive

Backups don’t stop cyberattacks, but they make recovery quick and stress-free. A recent backup allows you to restore your website after malware infections, failed updates, accidental deletions, or hosting issues without rebuilding everything from scratch.

Why It’s Necessary

  • Restores your website quickly after a security incident.
  • Protects your content from accidental data loss.
  • Stores backup copies away from your hosting server.
  • Automates backups to reduce manual effort.
  • Supports reliable WordPress backup free with cloud storage.

8. Disable XML-RPC

XML-RPC is rarely needed on modern WordPress websites, yet it remains a popular target for attackers. Disabling this unused feature removes a common attack vector and strengthens your website without affecting normal day-to-day functionality.

Why It’s Necessary

  • Blocks a frequently exploited attack method.
  • Reduces opportunities for brute-force login attacks.
  • Improves overall website security with a simple change.
  • Doesn’t affect most business websites or blogs.
  • Check with your developer if remote publishing is enabled.

9. Harden WordPress Files. No Code Knowledge Required

Strong security starts with secure website files. Basic WordPress file hardening practices, including disabling the built-in file editor and applying correct file permissions, reduce the chances of unauthorized changes while making your website more resilient against attacks.

Why It’s Necessary

  • Prevents unauthorized editing of plugin and theme files.
  • Reduces accidental code changes by users.
  • Limit file access using recommended WordPress file permissions.
  • Complements other security measures instead of replacing them.
  • Strengthens your website’s overall defense strategy.

10. Connect Google Search Console for Free Security Monitoring

Not every security issue is immediately visible. Google Search Console continuously monitors your website and notifies you about malware, phishing attempts, manual actions, and other problems that could impact your visitors and search visibility.

Monitoring search visibility is equally important. Our Technical SEO Services help identify indexing issues, crawl errors, and technical problems before they affect rankings.

Why It’s Necessary

  • Sends alerts when Google detects security issues.
  • Helps identify malware before rankings are affected.
  • Monitors manual actions and indexing problems.
  • Protects your website’s reputation and organic traffic.
  • Requires only a few minutes to set up and monitor.
  • Google also warns you if malware causes Safe Browsing issues.
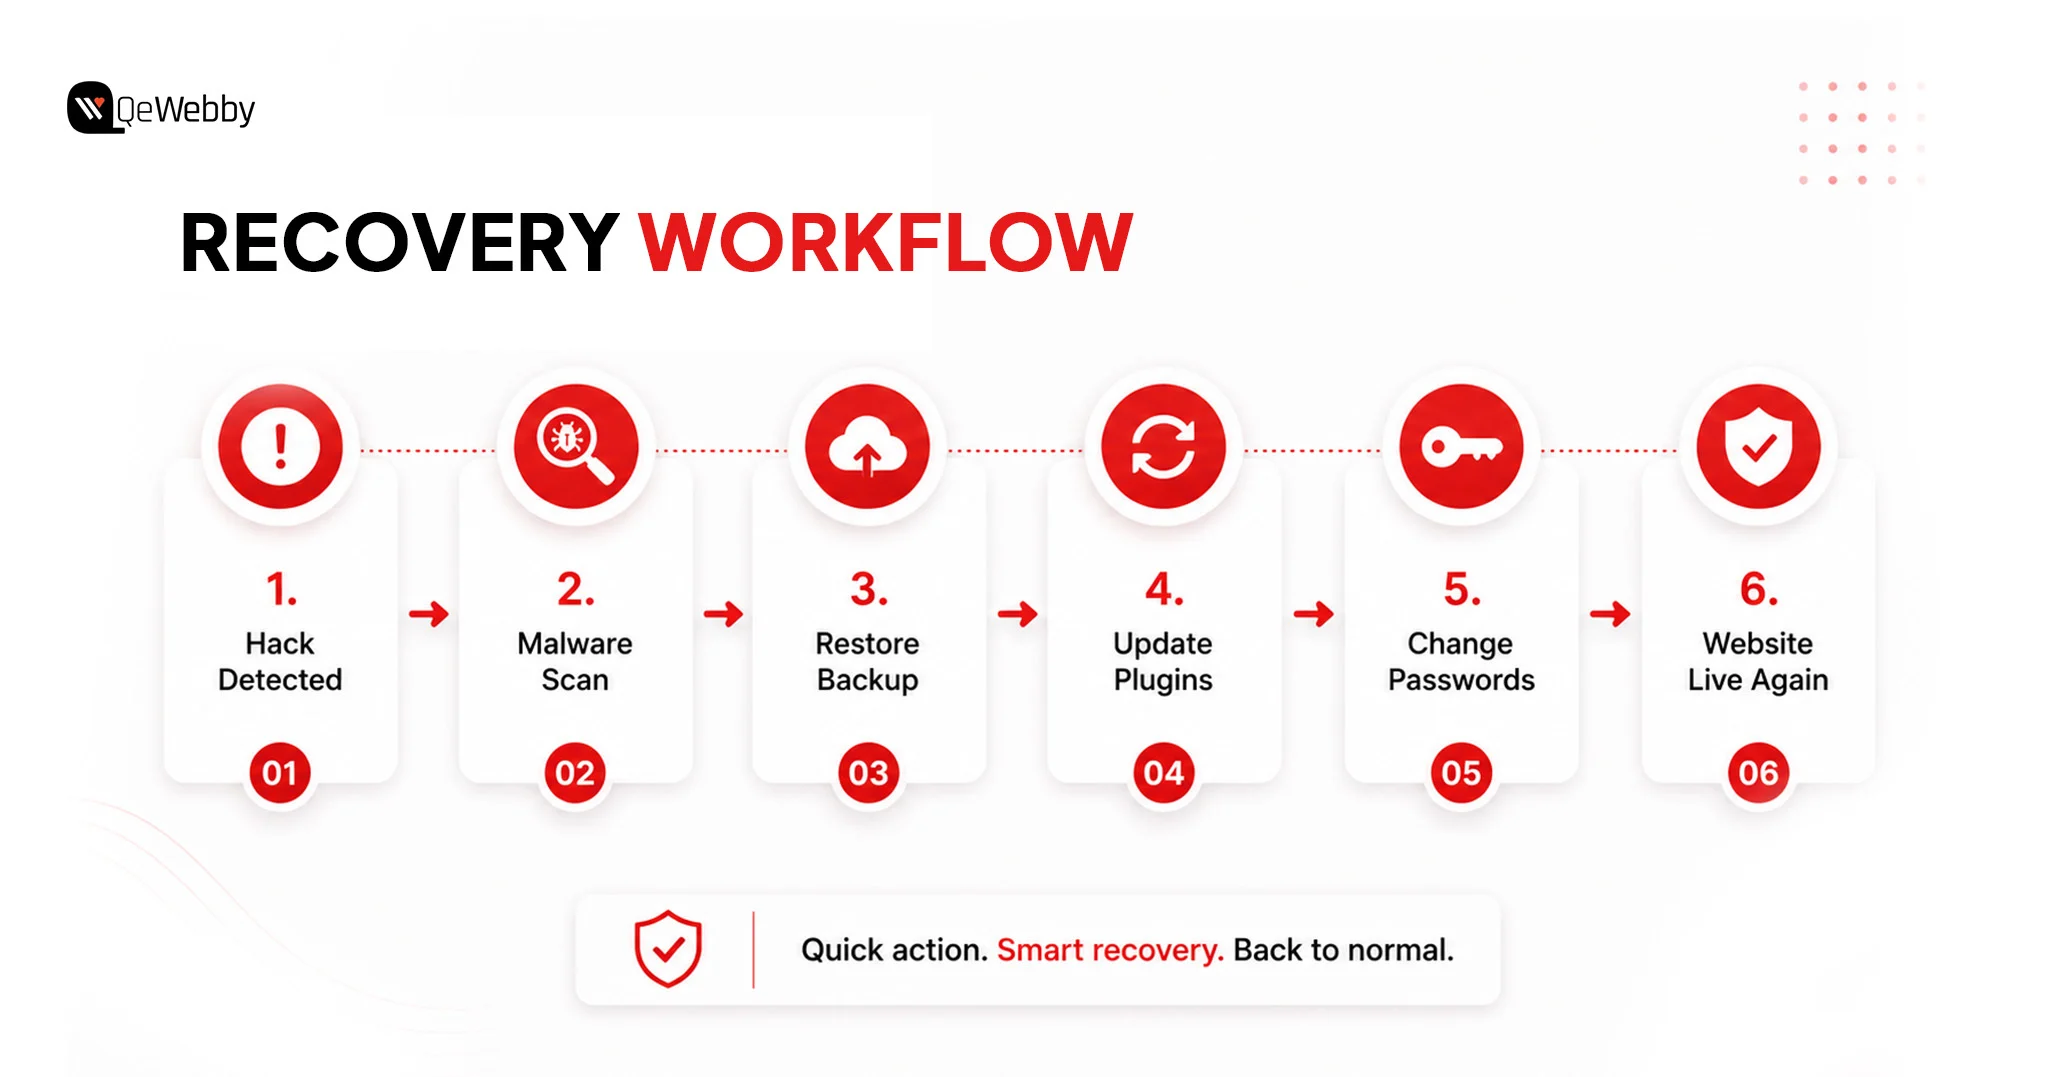
 

Recovery Workflow

3 Mistakes Small Business Owners Make With Free Security Tools

Installing free security tools is a great start, but using them incorrectly can create new problems. These are the three mistakes that leave many small business websites vulnerable, even when they believe they’re fully protected.

Mistake 1: More Security Plugins Doesn’t Mean More Security

Running multiple security plugins might seem like extra protection, but it often creates conflicts. One plugin’s firewall can interfere with another’s login protection, leading to false alerts, broken functionality, or even locking legitimate users out of the dashboard.

What to do instead

  • Install Wordfence as your primary security plugin.
  • Configure its firewall, malware scanner, and login protection correctly.
  • Avoid installing additional security plugins that perform the same tasks.

Mistake 2: Treating Security as a One-Time Setup

Many website owners secure their WordPress site once and never look back. Meanwhile, plugins receive updates, new vulnerabilities emerge, and your website gradually becomes less protected without you noticing.

What to do instead

  • Spend 15 minutes each month reviewing your security.
  • Update WordPress, plugins, and themes.
  • Check Wordfence scan reports.
  • Confirm that your automated backups completed successfully.

Mistake 3: Assuming Your Backup Will Work

A backup only has value if it can actually restore your website. Many businesses discover their backup is incomplete or corrupted only after a hack or server failure, when it’s already too late.

What to do instead

  • Download your latest backup once every quarter.
  • Perform a test restore on a staging website.
  • Verify that files, media, plugins, and the database restore correctly before you actually need them.
Book a Free Call

The Monthly 15-Minute Security Routine for Small Business Owners

The easiest way to maintain WordPress security for a small business is to spread small tasks across the month. Instead of spending hours fixing problems later, dedicate just a few minutes each week to keeping your website healthy.
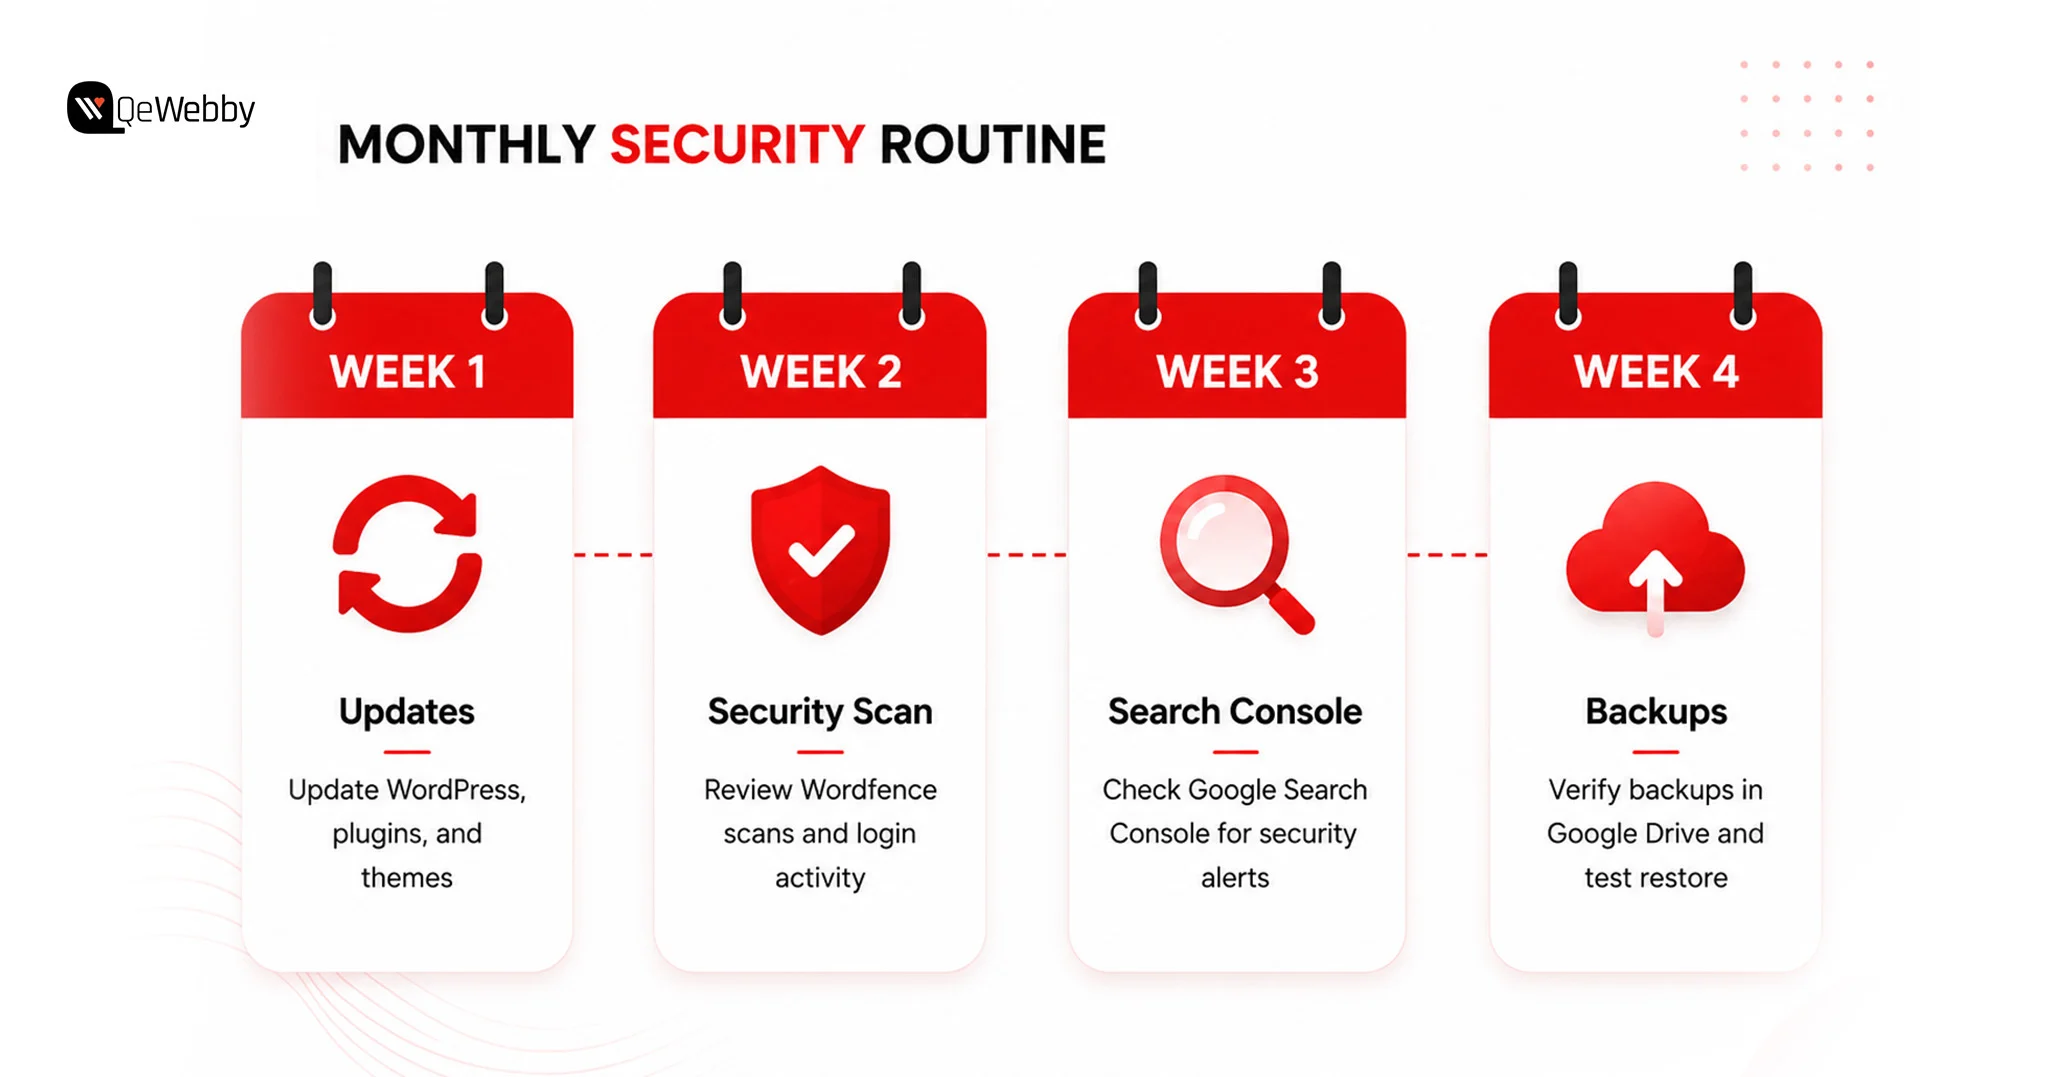
Monthly Security Routing

How QeWebby Can Help You Secure Websites?

Every security layer needs to be configured correctly, monitored regularly, and maintained as your website evolves. QeWebby helps businesses build a stronger security foundation with practical solutions that keep websites protected, reliable, and easy to manage.

  • Security Setup: We configure essential WordPress security features, including firewalls, malware protection, login security, SSL, backups, and file hardening to reduce common vulnerabilities from day one.
  • Proactive Protection: Our team continuously follows security best practices, helping your website stay protected against emerging threats instead of reacting after an attack occurs.
  • Website Maintenance: With our WordPress website maintenance service, we handle updates, monitor website health, review backups, and ensure plugins and themes remain secure and compatible.
  • Performance & Security Balance: A secure website should also perform well. We optimize your WordPress environment to maintain speed, stability, and security without compromising the user experience.
  • Security Designed for Small Businesses: Our WordPress security service for small businesses is designed to provide enterprise-level protection in a practical and cost-effective way, giving growing businesses the confidence to focus on their customers instead of website security.

Conclusion

Website security isn’t just about preventing attacks. It’s about protecting your reputation, customer trust, and long-term business growth. A secure WordPress site protects your reputation, strengthens customer confidence, and supports consistent online growth, making it an essential part of your digital presence rather than just another maintenance task.

Our professional WordPress Development Services combine security, performance, and long-term website management to help businesses build reliable digital experiences.

If you’re ready to strengthen your WordPress website with confidence, contact us to discuss the right solution for your business.
Security Review

WordPress Maintenance vs Managed Hosting: What’s the Difference and do You Need Both?

A WooCommerce checkout breaks after a plugin update. Your theme stops rendering correctly on mobile. Customers cannot complete purchases. You contact your hosting provider and receive a familiar response: “The server is running normally.”

That’s because managed hosting and WordPress maintenance solve different problems. Hosting keeps the infrastructure online. Maintenance keeps the WordPress application functioning properly.

The server can be healthy while the website is broken.

At revenue-generating sites, there’s no choice of words. Managed hosting is not the same as WordPress maintenance; where one stops, the other begins.

What is WordPress Maintenance?

WordPress maintenance services are regular maintenance schedules that control all the elements above the server: Plugins, themes, core files, database integrity, and security. This is typically offered in monthly WordPress support packages, ranging from the level of your site to the amount of time you will receive support. The top layer is the application layer, and it is called the scope. Not the hardware that’s under it.

That’s something many website owners don’t realize. Managed hosting is responsible for keeping the server online, while comprehensive WordPress maintenance services focus on keeping the website itself secure, updated, optimized, and functioning properly. They solve different problems at different layers of the stack.

What’s inside a WordPress maintenance plan:

  • All plugin updates are also tested in a ‘staging’ environment before being deployed to production. This is the one thing that most managed hosting plans out there don’t have, and that’s why most of the site breakages can be attributed to plugin conflicts.
  • WordPress core updates include security fixes, as well as new features. These releases are also tested and scheduled by maintenance providers, instead of being pushed automatically to live environments where an unexpected release may break any custom functionality.
  • Theme updates, though it might seem otherwise, are more disruptive. Theme updates have the potential to mess up custom CSS, break layouts of page builders, and reset the header/footer settings. A maintenance provider approves the visual rendering before the update gets to the live site.
  • Security monitoring includes malware scanning, login attempt monitoring, file integrity monitoring, and suspicious code injections. Partial scanning might be provided by managed hosts. The maintenance providers fix what they find.
  • Backups mean daily or real-time off-site copies with tested restore procedures. The operative word is tested. A backup nobody has verified isn’t a backup strategy. It’s an assumption waiting to fail at the worst possible time.
  • Performance checks address database optimization, image compression audits, plugin load time analysis, and wordpress seo performance optimization, including Core Web Vitals monitoring and page speed improvements. These aren’t optional maintenance tasks for revenue-generating sites. Slow-site degradation compounds quietly until it starts costing conversion rates.

What is Managed WordPress Hosting?

Managed WordPress hosting isn’t a premium tier of generic hosting. It’s a server environment built and operated specifically for WordPress workloads. The hardware, network architecture, and software stack are configured for WordPress, not shared across a hundred unrelated applications running on commodity infrastructure. Managed WordPress hosting pricing reflects that specialization, and the performance gap over self-managed VPS setups is real for any operator without a dedicated DevOps function.

What it does well, it does very well. Infrastructure-level performance and security sit in a different category from what most site owners can replicate independently. What it doesn’t do is touch the WordPress application running on top of that infrastructure. That boundary is where most buyers get into trouble.

What’s inside a managed WordPress hosting plan:

  • Server management covers operating system updates, server software patching, PHP version management, and hardware resource allocation. The provider owns this layer completely.
  • CDN serves content from edge nodes geographically close to each visitor, cutting page load times without any configuration on your end. Most managed hosts include CDN natively or through a Cloudflare integration.
  • Caching combines server-side page caching, object caching via Redis or Memcached, and opcode caching to absorb traffic spikes without creating database bottlenecks. This is where managed hosting earns its cost premium at scale.
  • Infrastructure security runs Web Application Firewalls, DDoS protection, IP reputation filtering, and network-level threat blocking. Outside-in protection: threats stopped before they reach WordPress. What it doesn’t cover is the application logic running inside.
  • Uptime monitoring backs a provider SLA, typically 99.9% at standard tiers and 99.99% at premium. The distinction worth noting: providers monitor their infrastructure. They don’t monitor whether your site is functioning correctly on top of it.

WordPress Maintenance vs Managed Hosting Comparison

Put these two services side by side, and the gaps become obvious. The confusion in the market isn’t about what managed hosting does; it’s about what it doesn’t do, and whether buyers notice that absence before something breaks.

Feature Maintenance Managed Hosting
Plugin Updates Full (staged) Limited (automated only)
Core Updates Tested Partial (auto-push)
Backups Off-site, tested Server-level
Hosting Infrastructure Not included Full management
Malware Monitoring Detect + Remediate Partial (detect only)
Technical Support App-layer issues Server-layer issues
Database Optimisation Included Not standard
Staging Environment Standard Sometimes included

Get a Free Consultation

Pricing Comparison in 2026

Understanding website maintenance cost versus managed WordPress hosting pricing separately is useful; understanding them together is more useful still. These are not competing budget lines; they cover different functions. Most growing businesses end up running both, which is why combined planning matters.

Monthly Cost Breakdown

Website Type Maintenance Managed Hosting
Small Business $20-$100/mo $20-$80/mo
Growing Business $100-$500/mo $50-$300/mo
Enterprise $500-$2,000+/mo $300-$5,000+/mo

What’s Included at Each Pricing Tier?

WordPress maintenance pricing and hosting costs don’t scale uniformly. What you’re actually buying at each tier is different in kind, not just in volume.

Budget tier ($20–$100/mo maintenance | $20–$80/mo hosting)

Automated backups, core and plugin updates, uptime monitoring, and monthly reporting. Support runs on a ticket system with 24–48 hour response windows. Hosting at this level covers shared or entry-level managed environments with CDN and basic caching. WordPress maintenance pricing here rarely includes staging environments, which means updates go straight to production untested. Workable for brochure sites and low-traffic blogs where a broken checkout isn’t a business event.

Growth tier ($100–$500/mo maintenance | $50–$300/mo hosting)

Staged updates are tested before deployment, malware remediation, performance optimization, priority support, and dedicated account management. Hosting shifts to dedicated resources with staging environments and faster SLA response times. This is where WooCommerce maintenance services typically land. Transactional sites carry update risk that budget plans aren’t built to handle. Staged testing and faster remediation aren’t upsell features at this level; they’re the baseline requirement for any site processing revenue.

Enterprise tier ($500–$2,000+/mo maintenance | $300–$5,000+/mo hosting)

Full-service maintenance with custom development hours, dedicated support engineers, SLA-backed response commitments, advanced security auditing, and proactive performance management. Hosting runs on isolated server environments with multi-region redundancy and enterprise-grade SLAs. Agencies operating white-label WordPress maintenance programs for multiple clients work in this tier. The pricing reflects accountability, not just capability.

Can You Use Managed Hosting and Maintenance Together?

Not only can you generate revenue from any site, but running both is the baseline standard. These services aren’t redundant. They cover different layers of the same stack, and the gap between those layers is exactly where sites break.

Why Hosting Doesn’t Replace Maintenance

Managed WordPress support at the server level tells you when the infrastructure is down. It doesn’t tell you when a payment gateway plugin conflict introduced during an automated update is silently failing your WooCommerce checkout. It won’t clean malware injected through a vulnerable contact form plugin. It won’t touch a database that has bloated to 2GB of autoloaded data.

According to WPScan’s WordPress Vulnerability Database, over 97% of WordPress vulnerabilities originate in plugins and themes, not the server. No managed host is scoped or paid to resolve application-layer problems. That’s a maintenance function.

Why Maintenance Doesn’t Replace Hosting

A maintenance provider manages your WordPress application on whatever server infrastructure you give them. If that server is under-resourced, misconfigured for WordPress workloads, or running on shared hosting with noisy neighbors throttling performance, plugin update management won’t fix it. Infrastructure constraints sit outside the scope of any care plan. A maintenance provider operating on a poorly configured server is competent work applied to the wrong constraint.

Best Combined Setup for Growing Businesses

The professional standard for revenue-generating sites: a premium managed host, WP Engine, Kinsta, Flywheel, or Cloudways, handling infrastructure performance, paired with a dedicated WordPress maintenance services provider managing the application layer. The host owns the server. The maintenance provider owns the site. Each vendor’s accountability is clear, and no coverage gap exists between them.

Agencies serving multiple clients often formalize this model through white-label WordPress maintenance programs, outsourcing application management to a specialist while retaining the client relationship. Maintenance labor is predictable at scale, and white-label providers price to reflect that predictability.

Businesses migrating from shared hosting often combine managed hosting with professional wordpress migration services before implementing ongoing maintenance.

WordPress Maintenance vs Managed Hosting: Who Is Responsible When Something Breaks?

Issue Managed Hosting Maintenance Provider
Server outage ✓ ✗
Plugin conflict ✗ ✓
Theme issue ✗ ✓
Database cleanup ✗ ✓
Malware cleanup Sometimes ✓
PHP updates ✓ ✗
Core Web Vitals optimization Partial ✓

Hidden Costs Most Website Owners Miss

Advertised WordPress maintenance pricing and managed WordPress hosting pricing are starting points, not total costs. Both categories carry expenses that only surface when something breaks or when the site outgrows its initial plan scope.

Maintenance costs that don’t appear in the plan:

Emergency fixes sit outside most WordPress support plans. Urgent remediation for a broken WooCommerce checkout during a product launch typically runs $200 to $500 per incident, billed separately from the monthly care plan.

Malware cleanup follows the same pattern: basic plans detect the problem; remediation, especially forensic cleanup across hundreds of pages of injected SEO spam, is a separate line item.

Custom development is another gap buyers miss. Care plans cover updates and monitoring. When a plugin conflict requires a code-level fix, that’s development work billed outside the plan entirely. Content updates follow the same logic: most maintenance plans don’t include them, and assuming otherwise leads to invoices that weren’t in the budget.

Hosting costs that don’t appear in the plan:

Traffic overages are the most common surprise. Plans price at bandwidth or visitor thresholds, and a product launch or press mention driving 10x normal traffic can generate overage charges that exceed the monthly plan cost.

According to Kinsta’s managed hosting documentation, overages are calculated per visit above the tier limit, which compounds quickly under unexpected traffic spikes. Storage upgrades hit media-heavy sites faster than expected, priced per increment with no retroactive adjustment.

Migration costs add a one-time $150 to $500 charge when switching hosts, regardless of “free migration” language in the plan terms, which typically applies to one site, one direction, one time.

The pattern across both categories: the advertised price covers the predictable scenario. Every edge case is an add-on.

Which Option is Right for Your Business?

The answer depends less on budget than on what’s currently broken and what failure mode you’re most exposed to. A slow server is a hosting problem. A plugin conflict is a maintenance problem. Most sites eventually face both.

Choose Maintenance If:

  • You’re already satisfied with your hosting performance and uptime
  • You need to update management and staged deployment to prevent site breakages
  • You need ongoing managed WordPress support for plugin conflicts, security incidents, and troubleshooting
  • You’re running a complex plugin stack where automated updates carry genuine risk

Choose Managed Hosting If:

  • Your current host is slow, and performance is the primary complaint from users
  • You’re experiencing uptime instability or unplanned outages
  • You need infrastructure-level support: server configuration, PHP versions, caching
  • You’re migrating from shared hosting and need a WordPress-optimized environment

Choose Both If:

  • You operate a revenue-generating website where downtime has a direct cost
  • You run a WooCommerce store. WooCommerce maintenance services plus managed hosting is the minimum viable setup for transactional sites.
  • You’re an agency managing multiple client sites and need reliable, scalable coverage.
  • You run a membership platform, LMS, or subscription site where application stability is critical.

Schedule a WordPress Audit

Typical Service Provider Categories

The market for both services has stratified significantly. Knowing which provider type fits your situation prevents overpaying for complexity you don’t need or underinvesting in coverage that matters.

DIY Maintenance Tools

With plugins such as ManageWP, MainWP and WP Umbrella, technically competent operators will have dashboard control over updates, backups and uptime monitoring for multiple sites.

They are suitable for the developer/agency who wants control but not the expense of a managed care plan. The downside of this is that human decision-making and remediation continues to rest on the operator.

WordPress Maintenance Agencies

Full-service WordPress maintenance companies can provide updates, security surveillance, custom development, content assistance, and more. They’re ideal for companies looking to have one place to monitor the health of applications, but that they don’t have to create it themselves. Basic plans are $50 per month, enterprise level is $2,000+/month.

White-Label Maintenance Providers

White label WordPress maintenance services are the same services provided under a different name, often by a web design agency who would like to offer maintenance services under their own brand without having to create an internal maintenance service. The agency is responsible for the client relationship, the white-label provider is responsible for the work. For agencies with 10+ client sites, the financial sense of outsourcing maintenance becomes clear, and this model makes sense.

Managed Hosting Providers

These providers, such as WP Engine, Kinsta, Flywheel, and Cloudways, prioritize infrastructure performance and reliability. The price of managed WordPress hosting from these providers starts at $20/month and can climb as high as $500+/month for enterprise-level hosting. Their value proposition is a (WordPress optimized) server stack, their scope is everything above the server layer.

Enterprise Hosting Platforms

For enterprises that have compliance needs, multi-environment workflows, and integration needs with DevOps, there are three options: Pantheon, Acquia, and WP VIP. These are platforms that combine hosting and maintenance capabilities with developer tools, pipelines and professional services and charge an appropriately high price with such capabilities.

WordPress Maintenance vs Managed Hosting: Final Decision Matrix

Most businesses complicate this decision by treating it as a single choice. There are two choices, one for each layer of the stack. Use this matrix to identify where you currently have gaps.

Scenario Recommended Solution
Brochure Website (low traffic, few plugins) Managed Hosting alone (handle updates manually)
Growing Business Site (10+ plugins, moderate traffic) Both maintenance + managed hosting
WooCommerce Store Both WooCommerce maintenance services + managed hosting are non-negotiable
Enterprise Site (compliance, high traffic) Both enterprise hosting platform + dedicated maintenance plan
Infrastructure Problems Only (slow server, outages) Managed Hosting upgrade
Application Problems Only (plugin conflicts, malware) WordPress maintenance services
Agency Managing Multiple Clients Both white-label WordPress maintenance + managed hosting per client

The Bottom Line

Managed hosting and WordPress maintenance services solve different problems at different layers of the same stack. Confusing one for the other is how revenue-generating sites end up exposed at exactly the layer nobody’s watching. The server being up doesn’t mean the site is working. For any business where downtime carries a real cost, the right question isn’t hosting or maintenance. It’s which provider owns which layer, and whether that accountability is clearly defined before something breaks.

9 WordPress Security Tips to Protect Your Website From Hackers

WordPress runs more than 43% of all websites on the internet. That dominance is what makes it the most targeted platform in the world.

Most site owners know security matters. Far fewer treat it as the ongoing, active discipline it actually needs to be. Attackers are not waiting for you to get around to it.

According to Patchstack’s State of WordPress Security 2025 report, 11,334 new vulnerabilities were identified in the WordPress ecosystem in 2025 alone. That is a 42% year-over-year jump. The median time between a vulnerability’s public disclosure and an attacker’s active exploitation is now just 5 hours.

This guide covers practical WordPress security tips that move the needle: regular updates, strong access controls, two-factor authentication, secure hosting, reliable backups, and a few hardening steps that most sites skip. By the end, you will have a clear WordPress security checklist you can act on today, not someday.

Why WordPress Security Is Critical?

WordPress’s dominance as a platform makes it the most targeted in the world, with new vulnerabilities primarily in plugins identified daily. Ignoring security can lead to persistent threats such as brute-force attacks and cross-site scripting (XSS), which often require no authentication to exploit. A breach is costly, resulting in lost search rankings, account suspensions, and high recovery fees, underscoring the necessity of proactive security measures.

The Platform’s Size Makes It a Permanent Target

WordPress does not get attacked because it is poorly built. It gets attacked because the math works out in the attacker’s favor. A single vulnerability in a plugin installed on 500,000 sites lets an automated scanner find and attempt to exploit it across all those sites within hours. That is a structural problem no individual site owner can solve at the platform level.

Ninety-one percent of vulnerabilities found in 2025 came from plugins rather than WordPress core itself, per Patchstack’s research. Core WordPress is actively maintained and patched quickly. The risk concentrates in the plugin ecosystem: vast, inconsistently maintained, and often abandoned by developers years before anyone notices.

Common Attack Types That Target WordPress Sites

The attack surface on a WordPress site is broader than most owners think. Brute-force login attempts are constant background noise on any public WordPress installation. SQL injection through vulnerable plugin forms still works reliably against unpatched sites.

Cross-site scripting (XSS) flaws in themes let attackers inject code that runs in your visitors’ browsers. And broken access-control vulnerabilities, which became the most-exploited class in 2025, let attackers perform admin-level actions with zero credentials.

43% of new WordPress vulnerabilities in 2025 required no authentication to exploit, according to Patchstack. An attacker does not need your password to use these vulnerabilities. They just need your site to be running an outdated plugin.

What Does a Breach Actually Cost?

A hacked site is not just a technical mess. Search engines blacklist compromised sites, wiping organic rankings that took months to build. Customer data exposure triggers regulatory consequences. Hosting providers suspend accounts when malware is detected. Rebuilding from a compromised state, without a working backup, regularly costs more in recovery time and contractor fees than a year of proper security maintenance would have.

Recovering lost rankings after a security incident can be a lengthy process, which is why security and WordPress SEO should be treated as complementary parts of a long-term website strategy.

Accenture’s State of Cybersecurity Resilience 2025 report found that only 1 in 10 organizations globally are adequately prepared to defend against current cyber threats. For small business site owners, that gap between confidence and actual readiness tends to be wider still.

Why Core WordPress Updates Are Non-Negotiable?

Regular updates are a fundamental security discipline, as every patch publicly announces a vulnerability that attackers immediately start exploiting. Core WordPress updates are non-negotiable, while plugin and theme updates require discipline and testing, ideally in a staging environment, to prevent compatibility issues while eliminating known vulnerabilities.

Every WordPress update that patches a security issue is, implicitly, also a public announcement of the vulnerability that was just fixed. The moment that announcement goes live, automated scanners start testing every site on the internet for the unpatched version. A site running an older WordPress release after a security patch is out is a visible, searchable target.

Updating WordPress core takes under two minutes through the dashboard. For sites where manual update management is not reliable, enabling automatic background updates for minor releases in wp-config.php is a straightforward hardening step. The line is:

define(‘WP_AUTO_UPDATE_CORE’, ‘minor’);

Plugin and Theme Update Discipline

Plugin updates require more judgment than core updates because they occasionally create compatibility issues. That said, leaving a plugin unpatched because you are worried about breaking something trades a certain risk for an uncertain one.

For businesses that do not have the time or technical resources to manage updates, backups, and monitoring internally, managed WordPress maintenance can help ensure security best practices are applied consistently.

A known vulnerability in an installed plugin is a guaranteed exposure. A compatibility issue from an update is a possibility you can test and roll back if needed.

The practical approach: maintain a staging environment to test updates before pushing to production. For agencies managing multiple client sites, this is standard practice. For individual owners, it is worth the setup time.

Use Strong Passwords and Manage User Roles Carefully

Weak passwords remain a reliable attack vector, not because attackers are especially sophisticated, but because so many sites still use them. Passwords for WordPress admin accounts should be at least 16 characters and include uppercase and lowercase letters, numbers, and symbols. Password managers like 1Password or Bitwarden generate and store these without requiring anyone to memorize them.

User role management is the piece most site owners skip. WordPress has five default roles: Administrator, Editor, Author, Contributor, and Subscriber. Every account on your site should have the minimum access level needed to do the job.

A copywriter who publishes blog posts does not need Administrator access. Giving it by default, for convenience, doubles your attack surface. If that account gets compromised, the role determines what an attacker can do with it.

Auditing your user list periodically takes about five minutes. Remove stale accounts. Downgrade roles that were set to Administrator without much thought. These are small actions that meaningfully reduce your exposure.

Implement Two-Factor Authentication (2FA)

Two-factor authentication is a login verification method that requires a second proof of identity beyond the password, typically a time-sensitive code from an authenticator app. Even if an attacker obtains a valid password through phishing or a leaked credential database, they cannot access the account without the second factor.

For WordPress, enabling 2FA on all Administrator and Editor accounts is one of the most efficient security changes available. Plugins like WP 2FA, Google Authenticator, or Wordfence’s built-in module handle this without custom development. Setting up a site with multiple admin users takes under half an hour.

One point that often gets missed: if your hosting provider offers 2FA at the hosting account level, enable it there too. A compromised hosting account bypasses WordPress entirely, granting direct file system access. The hosting layer needs to be as protected as the WordPress layer.

Two Factor Authentication

Install a Trusted Security Plugin and Configure It Properly

A WordPress security plugin is a monitoring and enforcement tool. It is not a passive, install-and-forget solution. Many site owners install one, see a green status dashboard, and assume they are covered. The plugin is only as useful as its configuration.

Wordfence Security, Sucuri Security, and iThemes Security Pro are three consistently solid options. Each provides a web application firewall (WAF), malware scanning, login attempt monitoring, and IP blocking.

Wordfence’s free tier is genuinely capable when configured correctly. The firewall needs to be in enforced mode, not learning mode, which it often defaults to after installation.

Regardless of which plugin you use, verify that the firewall is active in enforced mode, that malware scans run at least weekly, that login attempt limits are set, and that email alerts are active for high-severity events. A security plugin that generates no alerts and runs no scans is not protecting your site.

Use HTTPS and Choose Secure WordPress Hosting

Establishing a secure foundation for your site requires using HTTPS to encrypt data in transit and choosing a robust hosting environment. HTTPS is non-negotiable for security and search visibility. The choice of host determines the security floor, with managed WordPress hosting offering isolation and server-level protection that significantly reduces the risk inherent in shared hosting environments.

HTTPS Is the Baseline, Not an Advanced Feature

HTTPS encrypts data transmitted between your visitors’ browsers and your server. Without it, passwords, contact form submissions, and other data travel across the network as readable plain text. Search engines have treated HTTPS as a ranking signal since 2014. In 2025, a site running HTTP has both a security gap and a search visibility disadvantage.

Most reputable hosting providers include free SSL certificates through Let’s Encrypt. Installation is typically a single click in the hosting control panel. If your site still runs on HTTP, this is the first item to address.

Your Hosting Environment Sets the Security Floor

The quality of your hosting environment determines how much protection you can build on top of it. Shared hosting environments pool resources across thousands of accounts. A vulnerability in another tenant on the same server can, in some configurations, expose your files. That cross-contamination risk sits outside your control.

Managed WordPress hosting from providers like Kinsta, WP Engine, or SiteGround’s managed tier provides server-level firewalls, automatic malware scanning, PHP version management, and infrastructure isolation. The price premium over shared hosting is genuine. So is the security difference.

If your current hosting environment lacks modern security controls, migrating to a more secure infrastructure may be the safest long-term option. A structured WordPress migration ensures the transition happens without data loss or downtime.

Back Up Your Site Regularly and Test the Restoration Process

A backup is only valuable if it works when you need it. That point sounds obvious and gets ignored constantly. Many site owners discover that their backups were incomplete, pointing to an incorrect storage location, or simply broken, only when a breach makes restoration urgent.

The minimum for any WordPress security checklist: daily automated backups stored in at least two locations, one of which is off-site. Plugins like UpdraftPlus, BlogVault, or WP Time Machine handle scheduling and cloud storage integrations with services like Dropbox, Google Drive, or Amazon S3. Backup frequency should match the frequency with which your content changes.

Test it. Once a quarter, restore a recent backup to a staging environment and confirm the site loads, forms work, and no content is missing. That restoration test is the only way to know the process functions. Without it, you have a backup file that may or may not be usable when you actually need it.

Disable File Editing in the WordPress Dashboard

WordPress ships with a built-in code editor accessible through Appearance > Theme Editor and Plugins > Plugin Editor. It exists for convenience. It also creates a significant risk.

If an attacker gains access to any Administrator account, the file editor gives them direct access to your site’s PHP code through the dashboard. They can inject malware, plant backdoors, and modify core functionality without touching the server directly. Disabling the editor removes this escalation path entirely.

One line in wp-config.php does it: define(‘DISALLOW_FILE_EDIT’, true);

This does not affect any front-end functionality. Legitimate developers can still update files through FTP or server-side file management. The dashboard editor is the only thing removed, and it should not be used in production environments anyway.

Following secure development practices is equally important when making theme or plugin customizations. Experienced WordPress development services help ensure new functionality is implemented without introducing unnecessary security risks.

This is one of the most underused items on any WordPress security checklist. It takes thirty seconds and eliminates a meaningful category of post-breach damage.

WordPress Security Checklist: Quick Reference

  • Keep WordPress core updated
  • Update plugins and themes monthly
  • Use 16+ character passwords
  • Enable 2FA
  • Install a security plugin
  • Enable HTTPS
  • Use managed hosting
  • Run daily backups
  • Disable file editing
  • Remove unused plugins
  • Limit login attempts
  • Test backup restoration quarterly

Building a WordPress Security Checklist That Holds Over Time

A one-time hardening pass is not a security strategy. WordPress security problems compound when attention lapses: plugins get installed and forgotten, user accounts accumulate, backup schedules break silently, and hosting environments drift. Maintenance has to be ongoing; otherwise, it does not hold.

A working WordPress security checklist for ongoing maintenance looks like this: monthly review of user accounts and roles, monthly verification that all plugins and themes are up to date, quarterly backup restoration tests, quarterly review of security plugin logs for unusual activity, and annual review of the hosting environment and SSL certificate status.

For agencies managing client sites, this checklist should be included in a service agreement. For individual owners, a recurring calendar reminder is enough. The discipline matters more than the tool you use to track it.

Many agencies incorporate these security processes into their white-label WordPress development workflows, helping clients maintain secure, well-managed websites without expanding internal technical teams.

The Sites That Get Hacked Are Not Unlucky. They Are Unprepared.

The WordPress security tips in this guide are not advanced. None of them requires deep technical knowledge. What they require is consistency: keeping software current, managing access with intention, maintaining tested backups, and using the right tools configured properly.

Most breached sites in 2025 were not under-resourced. They were under-prioritized. Security was something to get to later, and later arrived at the wrong moment.

If you manage your own WordPress site, the WordPress security checklist above gives you a concrete place to start. If you manage sites for clients, these practices are the standard they are paying you to uphold.

And if you want professional WordPress security services that treat this as an ongoing discipline rather than a one-time task, QeWebby’s WordPress team is built to do exactly that.

That Get Hacked Today

Migrate Your WordPress Sites: A Definitive Guide [Easy & Fast]

Over 43% of the web runs on WordPress, yet the moment someone needs to migrate a WordPress site to a new host, the process feels anything but routine.

The fear is legitimate.

A failed WordPress migration does not just break a website. It can affect SEO rankings, form submissions, analytics tracking, checkout functionality, and customer trust within hours.

According to W3Techs WordPress Usage Statistics, WordPress powers more than 43% of all websites globally, making migration reliability a critical operational concern for businesses of every size.

What most migration guides miss is that failure rarely happens during the transfer itself. It usually happens before the migration begins or after the new site goes live.

This guide covers the complete process, including:

  • pre-migration preparation
  • plugin-based migration
  • manual migration
  • SEO preservation
  • downtime prevention
  • post-launch validation
  • common troubleshooting scenarios

So you can migrate your WordPress website safely without damaging performance, visibility, or user experience.

Pre-Migration Checklist: What to Do Before You Start

The WordPress site migration checklist isn’t administrative busywork. Every item on it represents a failure mode caught in advance, rather than a recovery task you’ll face under pressure with a live site down. Skipping even one step can mean a corrupted database, missing media files, or an SSL mismatch that takes days to trace.

#1. Build Your WordPress Site Migration Checklist Around a Full Backup First

A full site backup means your database export (.sql file) AND your complete WordPress file directory, including wp-content, all themes, all active plugins, and your .htaccess file.

There are many tools that let you store backups to Google Drive, Dropbox, and Amazon S3. Run a fresh backup immediately before migrating, not the one from yesterday. The few minutes this takes pays off the moment something breaks mid-transfer.

#2. Create a Staging Environment Before Any Live Migration Work

A staging environment is a private, non-indexed copy of your site hosted on a subdomain or locally, where you can test the migrated version before switching DNS. Managed hosts like Cloudways, SiteGround, and WP Engine offer one-click staging environments.

If your current host doesn’t, set one up by pointing a subdomain at a temporary directory. Testing on staging catches the majority of migration errors before they touch your live site.

#3. Audit Your Plugin Stack, Theme Dependencies, and PHP Version

Check the PHP version your current site runs on and confirm your new host supports the same version. Plugin conflicts post-migration are frequently traced back to PHP version mismatches, not the migration process itself.

Deactivate any plugins you no longer use before migrating: fewer files, smaller export, and a cleaner environment on the new host. This step alone reduces migration time noticeably on sites with bloated plugin libraries.

#4. Document Your Current SEO Configuration as a Baseline

Record your current permalink structure, sitemap URL, and robots.txt setup. Screenshot your Google Search Console coverage report. These become your post-migration benchmarks.

A spike in 404 errors or crawl anomalies in Search Console within 48 hours of going live on the new host is the signal to investigate; a clean baseline tells you exactly what changed.

talk-to-a-migration-expert

How to Avoid Downtime During WordPress Migration

DNS propagation issues, incomplete file transfers, or untested staging environments usually cause downtime during a WordPress migration. The safest migrations reduce risk before the DNS switch happens.

Practical Steps to Reduce Downtime
  • Lower DNS TTL 24 hours before migration
  • Complete all testing inside a staging environment
  • Keep the old hosting account active during propagation
  • Verify forms, images, redirects, and SSL before switching DNS
  • Schedule migrations during low-traffic hours
  • Avoid making content changes during migration windows

A properly planned migration often completes with minimal or no visible downtime for users.

Choosing the Right Migration Method

When Plugin-Based Migration Is the Smarter Call

Plugin-based migration handles file transfer, database export, import, and URL rewriting in a single coordinated workflow. For most site owners and small agencies, a WordPress migration plugin reduces a four-hour manual process to approximately 45 minutes.

Duplicator, with over 1 million active installs and a 4.9-star rating on WordPress.org, is the most commonly used tool for this. All-in-One WP Migration and Migrate Guru each cover the same core workflow with different trade-offs on file size limits, automation depth, and server-side processing.

The right choice depends on site size and technical comfort. All-in-One WP Migration works well for sites under 512MB with no technical configuration required. Duplicator’s free tier handles unlimited restore sizes and includes recovery tools. For large sites or multisite networks, Migrate Guru runs the migration on the server side, so your local machine never becomes a bottleneck.

When Manual Migration Gives You the Control You Need

Manual migration takes longer but gives you direct visibility into every layer of the process. Developers migrating sites with complex custom database tables, multisite configurations, or non-standard directory structures often find the manual route less prone to unexplained failures. If a plugin migration fails silently at the database import step, identifying which table caused it requires digging into logs. Manual migration makes every failure point explicit.

That said, manual migration is not inherently more reliable than a well-configured WordPress migration plugin. The reliability difference depends on the site’s complexity and your familiarity with phpMyAdmin, FTP, and wp-config.php, not on the method itself.

Best WordPress Migration Plugins in 2026

The right WordPress migration plugin depends on your website size, technical comfort level, and hosting environment.

Plugin Best For Key Strength
Duplicator Most WordPress websites Flexible and reliable migration workflow
All-in-One WP Migration Beginners Simple drag-and-drop interface
Migrate Guru Large websites Server-side migration handling
UpdraftPlus Backup-focused migrations Cloud backup integration
WPVivid Small-to-medium sites Easy scheduled backups and migrations

As per the WordPress Plugin Repository Duplicator reports over 1 million active installs, making it one of the most widely used migration tools in the WordPress ecosystem.

How to Migrate a WordPress Site Using a Plugin (Step-by-Step)

This walkthrough uses Duplicator, since it handles the widest range of site sizes, and the free version covers most common migration scenarios without file size restrictions on restores.

Step 1: Install and Activate Your WordPress Migration Plugin

Log in to your WordPress admin dashboard. Go to Plugins > Add New, search for Duplicator, install it, and activate. Once active, Duplicator appears in your left sidebar under its own menu.

Step 2: Create the Migration Package on Your Current Site

Click Duplicator > Packages > Create New. Run the pre-build scan to catch any configuration warnings: large files, oversized databases, and non-standard table prefixes. Name your package, run the build, and download both the installer file (.php) and the archive (.zip). Both files are required for the next steps. The installer file is useless without the archive.

Step 3: Prepare a Fresh Database on Your New Host

On your new host, create a MySQL database, create a database user, and assign full privileges. If your new host uses cPanel, the MySQL Databases section handles all three in under five minutes. Note the database name, username, and password; you’ll enter these during the Duplicator import step.

Step 4: Upload the Package Files and Run the Installer

Upload both Duplicator files to your new host’s root directory via FTP using FileZilla, or through your host’s cPanel file manager. Navigate to yoursite.com/installer.php in a browser. The installer walks you through database connection, archive extraction, and URL updating in a guided interface. Enter your new database credentials when prompted.

Step 5: Complete Your WordPress Site Migration Checklist Verification

After the installer finishes, log in to your new WordPress admin dashboard. Check that pages load, images display correctly, and no critical functions are broken. Run a URL search-replace if Duplicator didn’t handle it automatically; the Velvet Blues Update URLs plugin covers this. Update your DNS pointing to the new host only after this full verification step passes.

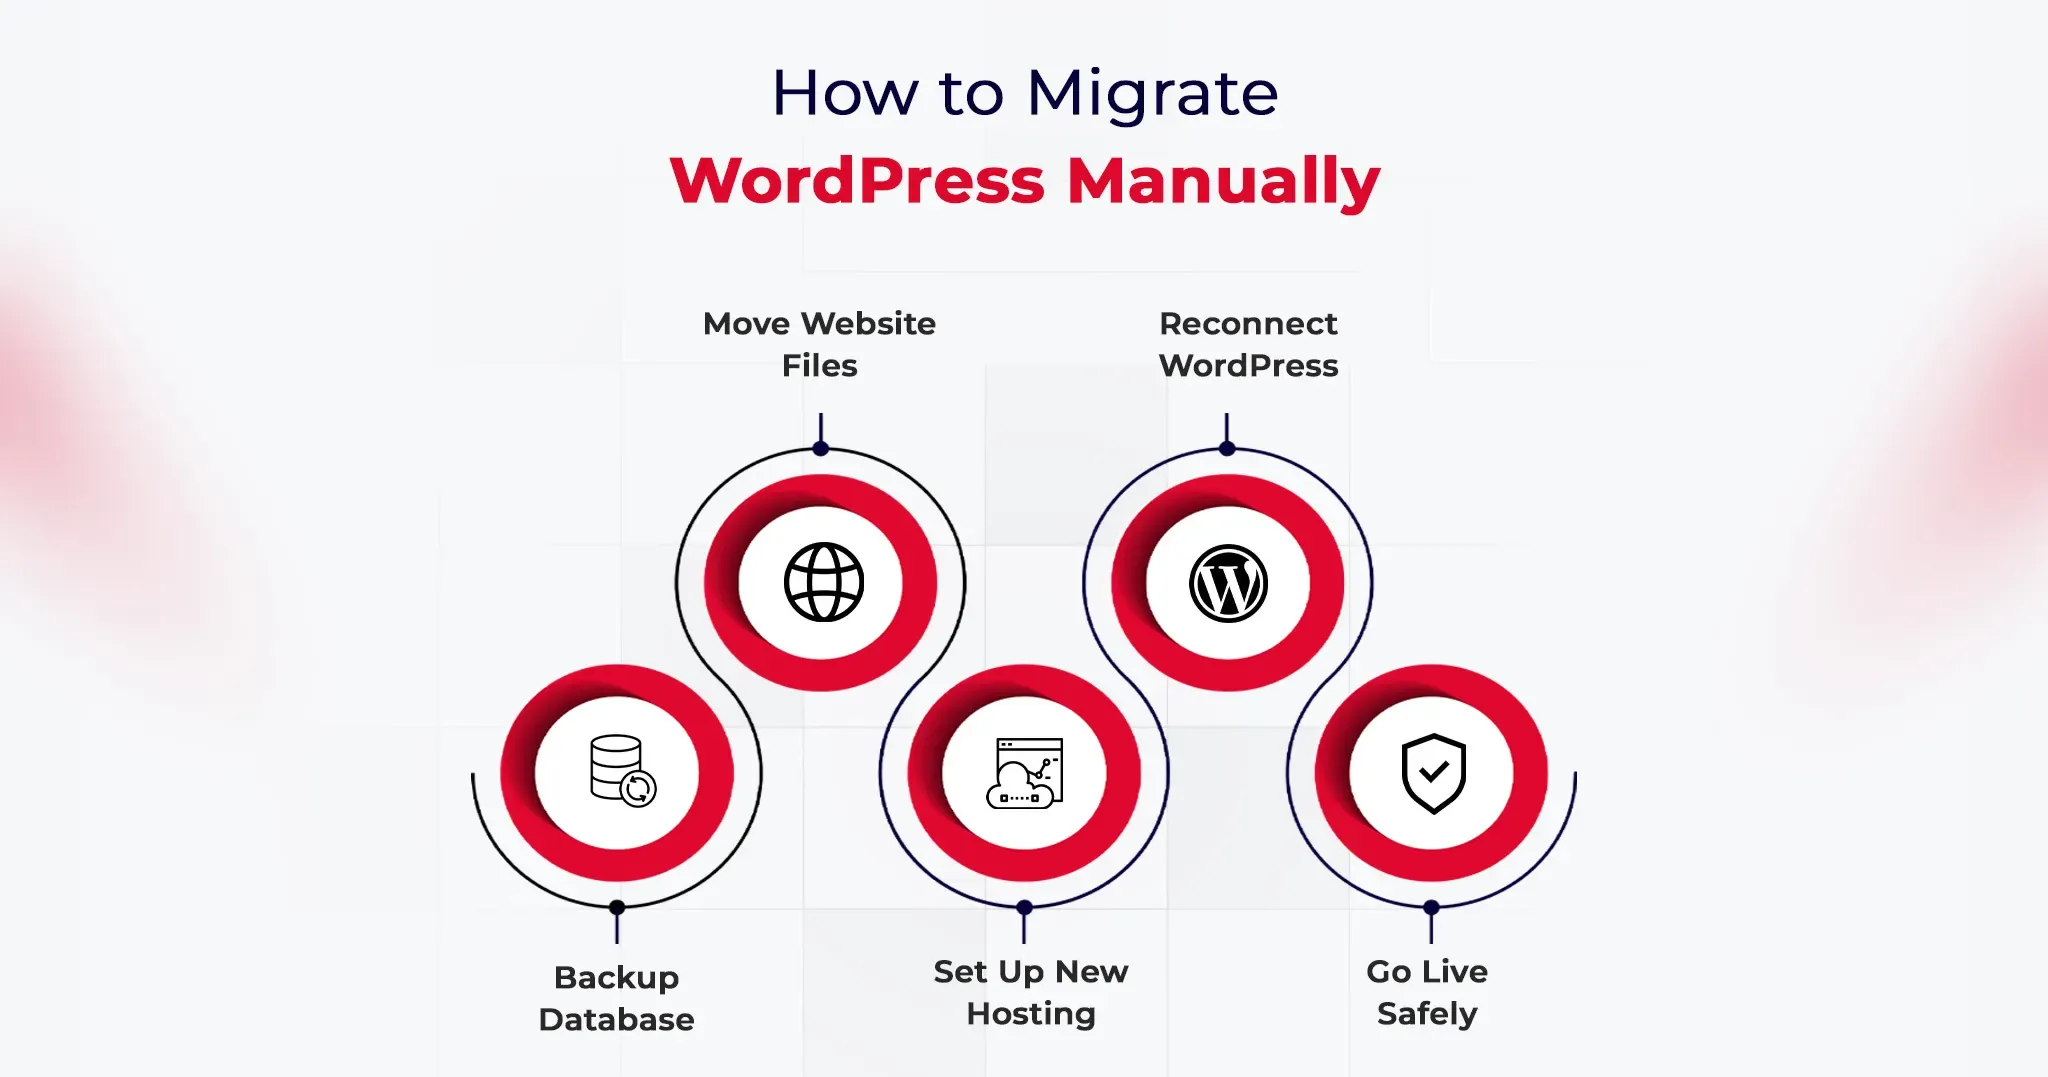
How to Migrate WordPress Site Manually (Step-by-Step)

Manual migration covers the same destination as the plugin method but gives you direct access to every component of the transfer.

Step 1: Export Your WordPress Database via phpMyAdmin

Log in to your current hosting cPanel and open phpMyAdmin. Select your WordPress database from the left panel, click the Export tab, choose the Quick export method, set the format to SQL, and click Go. Save the .sql file locally. This file contains every post, page, user, plugin setting, theme option, and WordPress configuration your site holds. Back it up separately before importing to the new host.

Step 2: Download All WordPress Files via FTP

Connect to your current server using FileZilla or an equivalent FTP client. Navigate to your WordPress root directory, typically public_html or www. Download the entire directory including wp-content, wp-includes, wp-admin, and the .htaccess file. Download time ranges from 15 minutes for a lean site to over an hour for wp-content folders heavy with media.

Step 3: Create a New Database on Your Destination Host

On your new host’s cPanel, open MySQL Databases. Create a fresh database, create a user, and assign all privileges to that user. Record the database name, username, and password precisely. The WordPress site migration checklist requirement at this step is exact credential matching: a single character mismatch between your wp-config.php and the actual database credentials will produce a database connection error.

Step 4: Import the Database and Reconfigure wp-config.php

Open phpMyAdmin on your new host, select the new empty database, click Import, and upload your .sql file. Once imported, open wp-config.php in a text editor and update DB_NAME, DB_USER, DB_PASSWORD, and DB_HOST to match your new database credentials. Upload the updated wp-config.php and all your WordPress files to the new host’s public root via FTP.

Step 5: Update URLs and Complete Your WordPress Site Migration Checklist

Navigate to your new site using the host’s temporary URL during the staging period. Run a database search-replace to update all instances of your old domain with the new one.

Better Search Replace handles serialized data correctly, which is critical for sites built with Elementor, Divi, or WooCommerce, where hardcoded URLs nest inside serialized arrays. Flush your permalinks by going to Settings > Permalinks and clicking Save Changes. That single action resolves approximately 90% of 404 errors that appear immediately after a manual migration.

how-to-migrate-a-wordpress-site-manually

How to Migrate WooCommerce Sites Safely

WooCommerce migrations require additional caution because they involve customer accounts, order data, payment gateways, and transactional functionality.

Important WooCommerce Migration Checks
  • Place the store in maintenance mode before migration
  • Backup WooCommerce orders separately
  • Test checkout and payment gateway functionality after migration
  • Reconnect Stripe, PayPal, and shipping integrations if needed
  • Verify transactional emails and automation workflows
  • Check product image references and inventory sync

Even when pages load correctly, payment or checkout issues can remain hidden until customers attempt purchases. That is why live transactional testing is essential after migrating WooCommerce websites.

Important Post-Migration Tasks You Shouldn’t Skip

The migration is not finished when the site loads correctly on the new server. These tasks are where most people create the problems they later spend hours debugging.

Verify SSL installation and HTTPS consistency. Confirm HTTPS works correctly on the new host. If your old host provisioned the SSL and your new host requires a fresh certificate, your site may load on HTTP but not HTTPS, which breaks any hardcoded HTTPS links stored in the database.

Recheck Google Analytics and Search Console tracking. Confirm your analytics tracking code fires on the new environment. If you changed domains, update your Search Console property and resubmit your XML sitemap to trigger a fresh crawl indexing the correct URLs.

Test every form, integration, and payment gateway. Contact forms, WooCommerce checkout flows, and third-party API connections (Mailchimp, Stripe, CRM hooks) need live testing. API keys and environment variables don’t transfer automatically, and a visual check of the page doesn’t confirm a form submission actually routes correctly.

Run a full crawl within 24 hours of going live. Screaming Frog or Sitebulb will surface broken internal links, redirect chains, missing image references, and duplicate content signals that a manual browse misses entirely. Even a 15-page site can return a crawl report with 30 actionable items.

Reduce DNS TTL 24 hours before the migration, not after. Lowering TTL to 300 seconds before you switch DNS means propagation completes in minutes rather than 24 to 48 hours. Set it back to 3600 once propagation confirms fully across major DNS resolvers.

WordPress Migration SEO Checklist

Moving a WordPress website without protecting SEO can quietly damage rankings, traffic, and indexed pages even when the migration itself appears successful. A structured SEO migration checklist helps preserve visibility and reduces the risk of crawl or indexing issues after launch.

Key SEO Checks Before and After Migration

  • Preserve the existing URL structure whenever possible
  • Configure 301 redirects for changed URLs
  • Verify canonical tags after migration
  • Re-submit your XML sitemap in Google Search Console
  • Review robots.txt configuration on the new environment
  • Monitor crawl errors and indexing coverage for at least two weeks
  • Check Core Web Vitals and page speed after DNS propagation
  • Validate internal links and image URLs after migration

According to Google Search Central, proper redirects and sitemap resubmission are critical steps when migrating websites without losing search visibility.

Even small migration errors like broken redirects or incorrect noindex settings can affect organic performance within days.

get-a-free-migration-consultation

Common Migration Issues and How to Fix Them

404 errors across all pages. Go to Settings > Permalinks and click Save Changes without modifying anything. This regenerates the rewrite rules in .htaccess and resolves the majority of post-migration 404 issues within seconds.

White screen of death after migration. This points to a PHP version mismatch or an exhausted memory limit on the new host. Check the server error logs first. If logs show a memory error, add define(‘WP_MEMORY_LIMIT’, ‘256M’); to wp-config.php. If logs show plugin errors, rename the entire plugins folder via FTP to deactivate all plugins at once, confirm the admin loads, then reactivate plugins one by one to isolate the conflict.

Images not loading after the transfer. Hardcoded image URLs in the database still reference the old domain. Run Better Search Replace, searching for your old domain and replacing with the new one, with the dry-run option turned off. Confirm the serialized data checkbox is enabled.

Database import timeout or file size error. Large .sql files frequently exceed phpMyAdmin’s default upload limit. Compress the file to .sql.gz before importing, or use a tool like BigDump for databases exceeding 200MB. Alternatively, import via SSH: mysql -u username -p database_name < backup.sql.

Admin login broken after migration. This is typically a cookie domain mismatch or a siteurl/home URL conflict. Add define(‘COOKIE_DOMAIN’, ”); to wp-config.php to reset the cookie domain configuration, then log in and correct the URLs under Settings > General.

Bonus Tips to Make WordPress Migration Even Faster

Use your new host’s free migration service. Per hosting industry data, 63% of managed WordPress hosting plans include free site migrations. Providers like Kinsta, WP Engine, and Cloudways move your site at no additional charge and handle technical edge cases that trip up self-managed migrations. For non-developers, this is consistently the fastest and lowest-risk path.

Move to NVMe-based hosting while you’re migrating. Sites migrated from SATA SSD to NVMe infrastructure typically see a 50 to 70% reduction in server response time (TTFB), according to hosting benchmark data from Hostingstep. If your migration is performance-driven, the hosting infrastructure choice matters more than the migration method you use.

Migrate during low-traffic hours. Schedule migrations between midnight and 6 AM in your site’s primary audience timezone. Any DNS propagation window falls during minimum traffic, errors surface before peak audience hours, and your monitoring tools catch anomalies before users do.

Use WP-CLI for databases over 1GB. WP-CLI, WordPress’s command-line interface, handles database exports, imports, and search-replace operations directly on the server, with no phpMyAdmin file size caps and no browser timeout risk. For any site with a database above 1GB, command-line tooling is the correct approach, not a browser-based phpMyAdmin interface.

Conclusion

Getting the process of how to migrate a WordPress site right is not primarily a technical challenge. It is a sequencing challenge. Full backup happens before anything else. The staging environment gets tested before DNS changes. The post-migration checklist runs before you announce the new site is live.

Whether you use a WordPress migration plugin like Duplicator or work through the manual FTP and phpMyAdmin method, the structure of the process matters more than the specific tools. Follow the sequence, test before switching DNS, verify after switching, and most migrations complete without incident.

book a free strategy call

Managed WordPress Maintenance vs DIY: What B2B Companies Need to Know

Managed WordPress maintenance is a service where a specialist team handles your site’s core updates, security monitoring, backups, and performance tuning on an ongoing basis so nothing falls on your internal team. It’s the standard choice for B2B companies where the website drives lead generation and downtime has a real cost. DIY maintenance, by contrast, works only when someone in-house has both the technical skill and the spare hours to stay on top of updates, threats, and backups manually. Below, we break down exactly what’s included in managed maintenance, what DIY really costs in time and risk, and how to decide which fits your business.

Managed WordPress maintenance is best for B2B companies that rely on their website for lead generation, security, and uptime, while DIY maintenance is suitable only for small or low-risk sites with in-house technical expertise and time to manage updates, security, and performance manually.

Many companies face the dilemma of whether to manage WordPress maintenance in-house or outsource it to specialists. While the DIY approach may seem cost-effective, it can quickly become a burden for stretched marketing and IT teams, especially as the complexity of plugins and cyber threats grows.

With over 300,000+ websites powered by WordPress, competition is high. Making regular updates, implementing security monitoring, maintaining backups, and optimizing performance are crucial. DIY maintenance demands technical expertise and constant attention, whereas outsourcing to trusted providers offers predictable performance, quicker issue resolution, and robust security.

This article will outline the pros and cons of each approach, helping B2B owners, IT managers, and digital marketers select the most suitable maintenance model to ensure business continuity and optimize site performance.

What Is Managed WordPress Maintenance?

Managed WordPress maintenance is a continuous process where a specialist team handles everything from core updates to theme changes, security monitoring, backups, performance tuning, and more. It differs from the DIY approach to handling updates, security, and bug fixes. This reduces the time and expertise required to run a website – how?

Managed WordPress maintenance often comes with hosting services bundles, which add to the WordPress-optimized infrastructure. It offers better scalability and ensures high availability for the site without disruptions. With such a service, you can provide predictable performance, strong security, and rapid bug fixes without the hassle of managing servers.

What’s Included in Managed WordPress Maintenance?

Managed WordPress maintenance typically covers:

  • Core, plugin, and theme updates — applied and tested automatically, not manually
  • Security monitoring — active scanning and threat response, not just a firewall plugin
  • Automated backups — with tested, quick-restore points
  • Performance tuning — server-level and site-level optimization
  • Uptime monitoring — with alerts before customers notice a problem

Most B2B providers bundle these into a monthly retainer ranging from $100–$500+ depending on site complexity versus the $0–$100/month in tools plus staff hours a DIY approach requires.

Who Should Choose Managed WordPress Maintenance?

Managed WordPress maintenance is recommended for:

  • B2B companies generating leads through their website
  • Sites with CRM, marketing automation, or gated content
  • Teams without dedicated WordPress engineers
  • Businesses requiring high uptime, security, and predictable performance
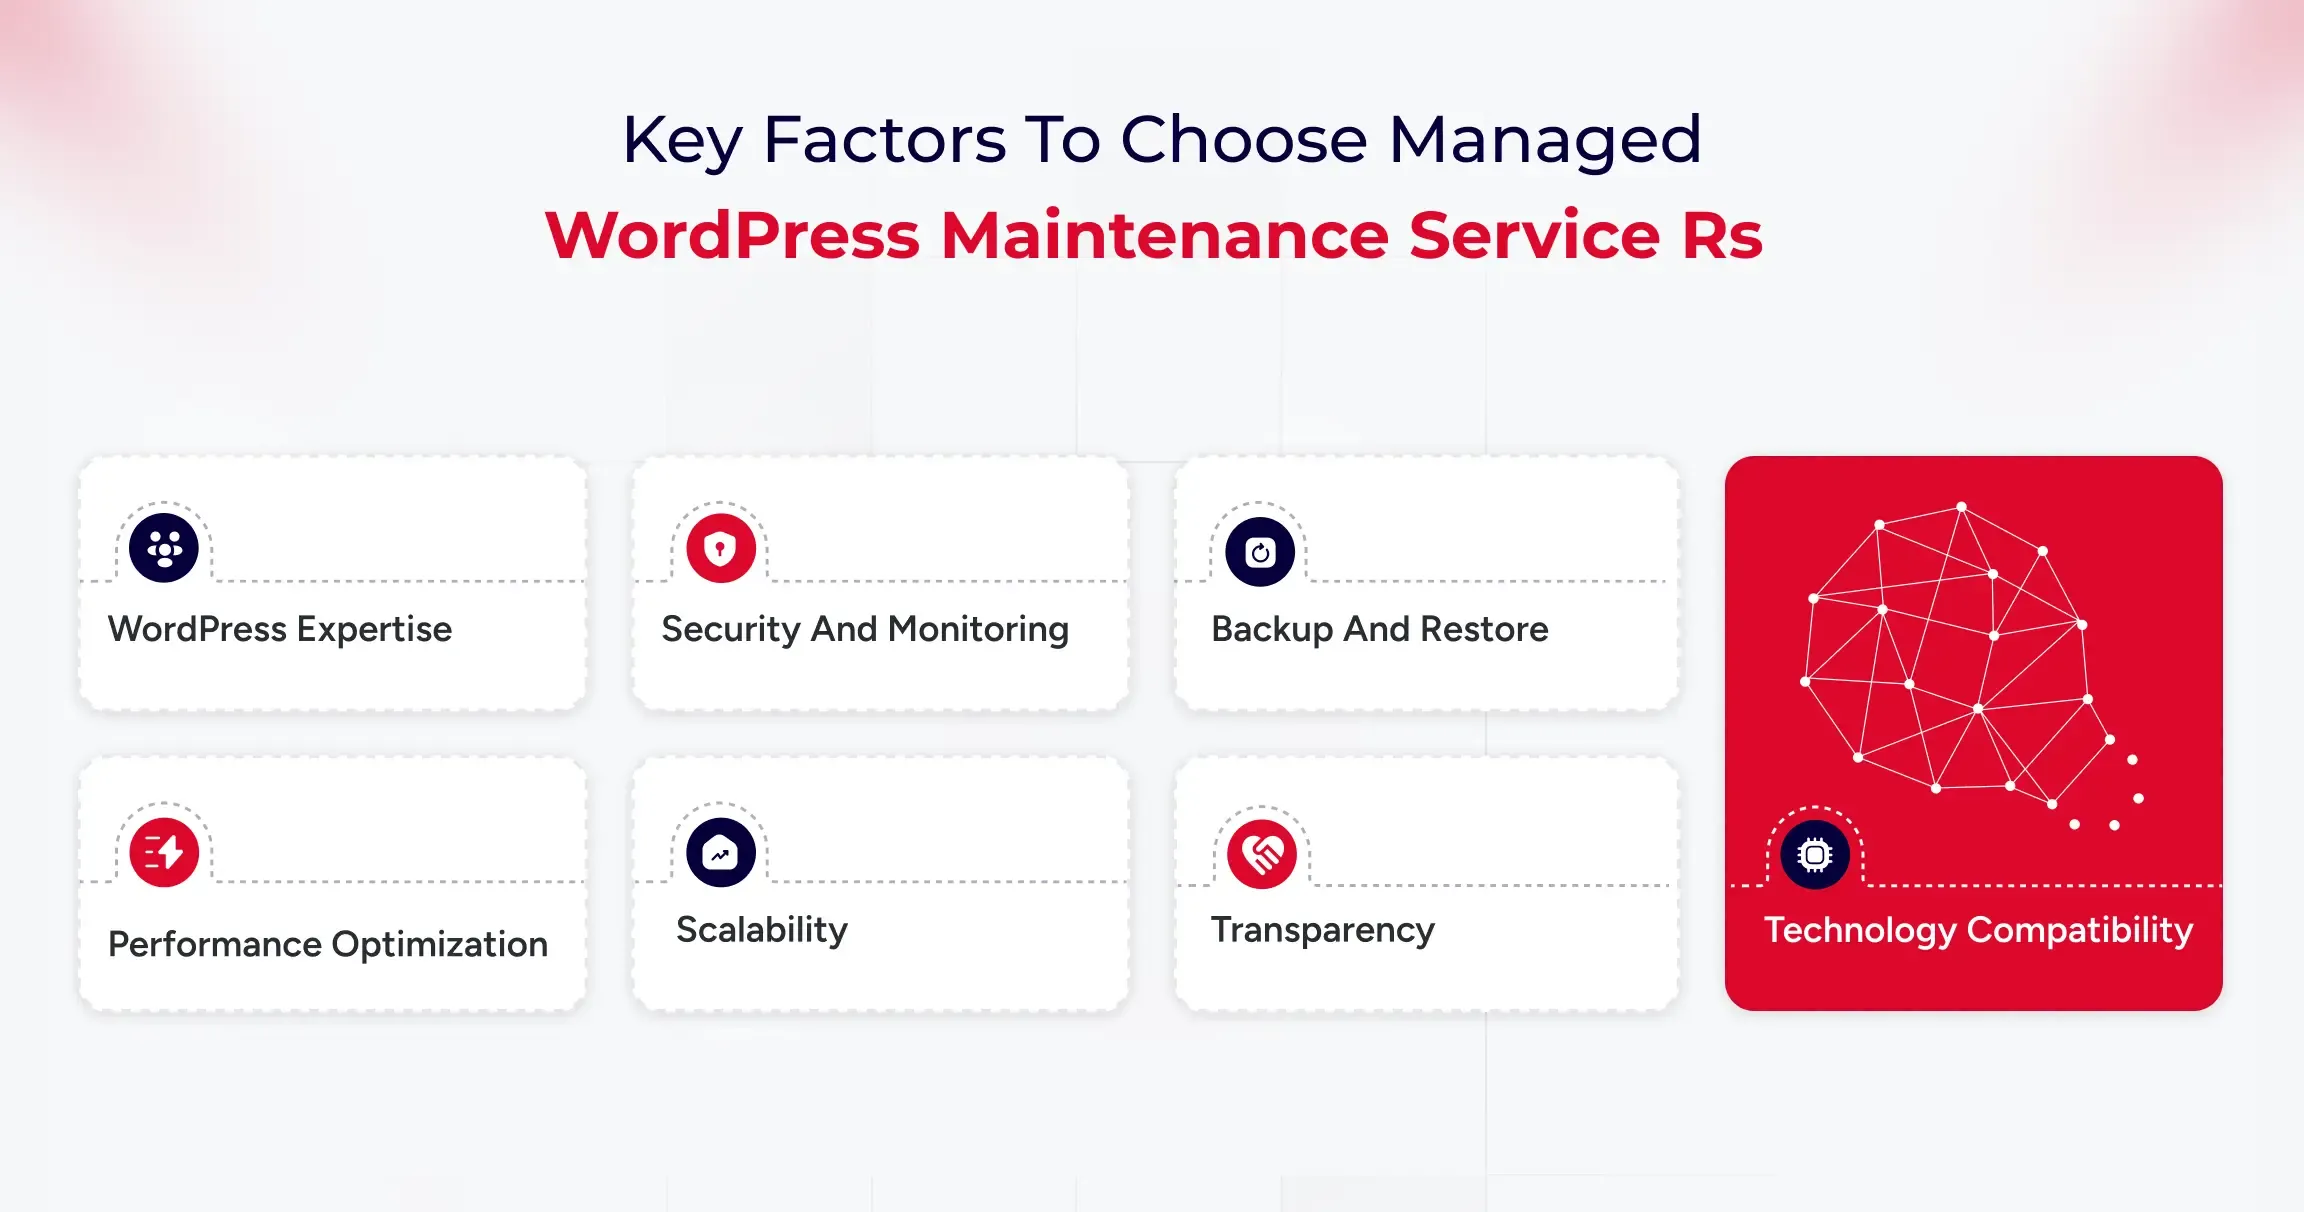
key-factors-to-choose-managed-wordpress-maintenance-service-company

Key Features of Managed WordPress Maintenance Services

  • Automated WordPress updates for core systems, plugins, and themes.
  • Regular site backups with quick restore points that ensure faster recovery in case of incidents.
  • 24/7 security monitoring with comprehensive malware scanning, firewall implementations, and multi-factor authentication.
  • Performance optimization for the website through server-level caching, CDN integrations, and database fine-tuning for faster loading.
  • Complete uptime and health monitoring of the website
  • Access to WordPress expert teams to resolve plugin conflicts, errors, and best practice applications.
  • End-to-end testing of the website, including staging environment configurations and automation.
  • Migration assistance and disaster recovery options

Pros of a Managed WordPress Maintenance Service

  • Managed WordPress maintenance services can help you save time and focus on content, growth, and business priorities.
  • Ensures better website security posture through continuous monitoring, regular updates, and established procedures.
  • Faster, more consistent performance via WordPress-tuned infrastructure and caching/CDN layers.
  • Expert, WordPress-specific support that shortens troubleshooting and reduces downtime.
  • Effortless scalability for campaigns and traffic spikes without manual capacity planning.
  • Peace of mind with automated backups and quick restores if something goes wrong.

Cons of a Managed WordPress Maintenance Service

  • Managed WordPress services can have a higher initial cost but offer more returns in the long term.
  • Businesses have less control over server configurations, advanced customizations, and plugins.
  • No flexibility to run different types of sites or migrate them to another CMS.
  • Some managed services are often limited to specific plugins, which can reduce your options.

What Does DIY WordPress Maintenance Involve?

DIY WordPress maintenance is an approach of taking full responsibility for your website’s care, updates, and performance without relying on any managed service. It requires hands-on management to ensure your WordPress site is up-to-date, secure, and runs smoothly. This includes regular updates, backups, performance checks, and troubleshooting to ensure optimal system performance.

Who Should Choose DIY WordPress Maintenance?

DIY maintenance may be suitable for:

  • Small, low-traffic sites
  • Teams with in-house WordPress expertise
  • Non-critical marketing websites

Key Features of DIY WordPress Maintenance Approach

  • Regular updates for WordPress core, plugins, and themes
  • Routine backups and testing restore points.
  • Security monitoring (utilizing plugins such as Wordfence or Sucuri).
  • Database cleanup and optimization.
  • Spam comment management and user account reviews.
  • Broken link checks and form testing.
  • Performance monitoring and error log review.
  • SEO audits and content updates.
  • Manual documentation and training for involved team members.

Pros of DIY WordPress Maintenance Approach

  • Complete control over server setup, plugins, updates, and customizations.
  • Lower cost, as you avoid fees charged by managed service providers.
  • Flexibility for advanced or unique technical needs, including specialized plugins or scripts.
  • Ability to optimize, experiment, and troubleshoot as needed.

Cons of DIY WordPress Maintenance Approach

  • Time-consuming and requires ongoing attention to detail.
  • Increased risk if security vulnerabilities, plugin conflicts, or errors go unnoticed.
  • Requires technical knowledge to troubleshoot, restore, and prevent major issues.
  • Mistakes during updates or backups can result in downtime or data loss.
  • No guaranteed expert support, leaving all maintenance and fixes up to the site owner.

Now that you know what managed WordPress maintenance is and the DIY approach to it, let’s compare them to understand which is best for you.

book-a-free-consultation

Detailed Comparison of Managed WordPress Maintenance vs DIY Approaches

Comparing managed WordPress maintenance services with a DIY approach requires consideration of cost, expertise requirements, security, performance, scalability, and support.

Key Differences at a Glance

The main difference between managed WordPress maintenance and DIY maintenance lies in responsibility, risk, and scalability. Managed services offer proactive security, automated updates, and expert support, while DIY maintenance requires manual effort, technical expertise, and carries higher operational risk as websites grow.

Let’s start with the cost considerations of using both methods for B2B companies.

Feature DIY WordPress Maintenance Managed WordPress Maintenance
Cost (Estimation) $0–$100/month $100–$500+/month
Time Commitment 5–15+ hours/month (staffed) Minimal (provider handles most tasks)
Required Expertise Moderate to high technical troubleshooting skills Minimal WordPress usage/familiarity
Security & Risk Manual, expertise-dependent; higher exposure Proactive, expert auditing, 24/7 monitoring
Performance Manual optimization; plugin/setup dependent Server, CDN, cache optimized by experts
Scalability & Support Poor, increasingly complex with growth Automated scaling, multi-site support

1. Cost Considerations for B2B Companies

Managed services typically cost $100- $500+ per month for enterprise-grade offerings. At the exact time, DIY costs are as low as $0-$100/month, depending on the type of plugins, tools, and internal staff support you may need.

Managed solutions provide bundled packages that include security updates, backups, support, and uptime guarantees. A DIY approach may be cheaper, but it often comes with hidden costs. For example, you need to hire in-house staff who can work dedicatedly on WordPress maintenance or divert existing staff from core business activities.

Especially for the complex B2B sites, managed WordPress maintenance services make more sense due to a predictable cost structure. DIY, on the other hand, is an approach where prices escalate with an increase in the technical complexity of the website.

2. Time Commitment and Required Expertise

DIY maintenance takes more time than managed services due to the extensive workforce needed. Regular security checks, updates, and patches can take days and even months with an in-house team. Plus, you may have restricted resources, which adds to the complexities of an already delayed process of WordPress maintenance.

3. WordPress Site Backups: Managed Service vs DIY

Ensuring you have proper backups is crucial, especially in the event of an incident or cyber attack, as it will help you recover quickly. DIY backups offer the benefit of complete control over backup configurations, but manually testing, removing, and adding backups can be tedious.

On the other side, a managed WordPress maintenance service ensures automation of the backup process. Set a daily schedule according to your requirements for the backup, and the system will automatically create a backup.

4. Plugins & Core Updates

If you choose the DIY approach, maintaining each plugin, ensuring timely updates, and security can be complex. For example, if you have multiple sites, you have to update plugins across all of them. This can increase manual efforts if you choose the DIY approach.

One of the key benefits of WordPress maintenance provided through managed services is the automation of plugin updates. Many WordPress website maintenance packages offer end-to-end plugin update automation by default.

Plus, managed hosting providers handle server maintenance, PHP updates, and server-side software. This means you can optimize core updates by outsourcing WordPress maintenance.

5. Performance Optimizations

Managed WordPress maintenance handles licenses and support, as well as pre-configuring all servers across sites for optimal performance. On the contrary, the DIY approach requires manual configurations, which are necessary to fine-tune site performance.

Each site may have unique challenges in terms of performance, loading time, and server management. Therefore, if you have multiple sites, managed WordPress maintenance is a sensible option.

6. Security And Risk Management

A DIY approach relies heavily on your internal team’s technical expertise. Routine tasks, such as malware scanning, patching vulnerabilities, configuring firewalls, and monitoring suspicious activity, must be performed manually and consistently to ensure optimal security.

Any delays or missed updates can expose your site to significant risks. Especially for B2B companies handling sensitive customer data, CRM integrations, or gated assets, these become crucial. Managed WordPress maintenance, however, offers a proactive security posture.

Providers run continuous 24/7 monitoring, apply real-time threat detection, and implement enterprise-grade firewalls and malware removal tools. Security patches are deployed instantly, reducing the attack window and minimizing operational disruptions. Most managed services also include incident response support, helping you recover quickly without diverting internal resources.

Security Verdict

For B2B websites handling customer data or lead funnels, managed WordPress maintenance provides significantly lower risk than DIY approaches due to continuous monitoring, faster patching, and expert incident response.

Now that you know the difference, it’s time to understand a step-by-step approach to WordPress maintenance.

How to Get Started with WordPress Maintenance

WordPress maintenance is a continuous process and needs constant monitoring. This is why you need to plan the entire maintenance. With a managed service, you don’t need to worry about planning or execution. However, if you choose DIY, you need to be mindful of specific tools and access permissions, which you will need before implementing the WordPress maintenance approach.

What You Need Before You Begin (Tools, Access, Resources)

First and foremost, you will require access to WordPress admin, hosting panel, SFTP/SSH, database (phpMyAdmin), DNS, and license portals for premium plugins/themes. You will need to install and configure a reliable backup plugin or service. Verify the off-site storage and ensure multiple copies of the site are stored at different locations. Other prerequisites are,

  • Add a reputable security plugin with a WAF, malware scanning, login security, and optionally two-factor authentication (2FA).
  • Create a safe sandbox to test updates and restores before deploying them to production, which is often included in various services and specialized tools, such as BlogVault workflows.
  • Monitor uptime alerts, performance metrics, and scan the site regularly for malware.

You have all the prerequisites. Now is the time to implement WordPress maintenance.

Step-by-Step Guide to Setting Up and Managing WordPress Site Maintenance

WordPress maintenance involves five ongoing tasks: backing up data, updating software, monitoring security, optimizing performance, and testing functionality. Managed services automate these tasks, while DIY approaches require manual execution and technical oversight.

how-to-set-up-maintenance-mode

Step 1: Back up your website

Think of a backup as a safety copy of your entire site, including both the visible content (themes, plugins, uploads) and the hidden infrastructure (the database with posts, pages, users, and settings). Set up automatic full backups on a schedule and store copies off-site (such as Google Drive, Dropbox, or a backup service) so you can restore if anything breaks or gets hacked.

Run a quick “test restore” occasionally to be sure those backups actually work before you need them in an emergency.

What to do in practice:

  • Install a reputable backup tool and schedule both file and database backups (daily/weekly, depending on how frequently your site changes).
  • Save backups to external storage and keep several recent versions for safety.
  • Make a quick note of restore steps so you’re not guessing during a crisis.

Step 2: Update themes, plugins, and core

Updates fix bugs, patch security holes, and improve compatibility, so keeping WordPress core, plugins, and themes current is one of the easiest ways to stay secure and stable. Before updating, ensure that a fresh backup exists. For larger or more complex sites, test updates on a staging copy first to avoid breaking live pages.

After updating, give the site a quick check to confirm layouts, forms, and key features still work as expected.​

What to do in practice:

  • Update weekly (or sooner for security releases), starting with plugins, then themes, then core if needed, while having a recent backup ready.
  • Remove plugins and themes you don’t use; fewer moving parts means fewer risks and faster pages.
  • For significant updates, consider delaying a couple of weeks if your site is sensitive, and test on a staging environment first to catch conflicts early.

Step 3: Monitor security and performance

Security monitoring identifies malware, suspicious logins, and known vulnerabilities, allowing you to respond quickly if something’s amiss. Enable basics like strong passwords, two-factor authentication, and limited login attempts, and use a security scanner to run routine checks automatically. At the same time, keep an eye on performance uptime alerts, page speed, and Core Web Vitals.

What to do in practice:

  • Turn on daily security scans and get alerts for downtime and unusual activity (user activity logs help pinpoint what changed and who did it).
  • Review speed weekly: large images, bloated plugins, and full caches can slow you down, so optimize images, purge cache, and prune heavy add-ons.
  • Set a cadence: daily automated scans/uptime checks, weekly performance updates, monthly backup tests, and a deeper audit for peace of mind.

Step 4: Review and test website functionality

After changes or on a regular schedule, click through your most essential paths like a visitor to ensure everything still works, such as menus, contact forms, checkout, and search. Check for broken links, missing images, and unusual layout shifts, as even minor issues can frustrate users or lead to lost conversions.

If something’s off, roll back using your latest backup or disable the last update to isolate the problem, then retest before going live again.​

What to do in practice:

  • Keep a short checklist: homepage load, key landing pages, forms, login, cart/checkout, and search.
  • Run a quick broken link and spam comment cleanup as part of routine maintenance to keep the site tidy and trustworthy.
  • If you manage multiple sites, consider using a central panel to view updates, uptime, and performance at a glance, saving you time.

How to Choose the Best Managed WordPress Maintenance Service for Your Company

When selecting a managed WordPress maintenance partner, consider it as finding a long-term team member. Your provider should offer consistent performance, strong security, reliable support, and a plan that aligns with your business goals.

For B2B organizations, it’s vital to choose partners that understand complex site setups and the need for smooth digital operations. A good service should require little involvement from your internal teams.

Updates, monitoring, backups, and performance tuning should happen regularly. The best providers keep your site stable and anticipate issues before they arise.

Key Factors to Consider

  • WordPress Expertise: Ensure the team has experience with enterprise-level WordPress and can handle plugin conflicts and performance optimization.
  • Security and Monitoring: Look for 24/7 threat detection, web application firewall (WAF) protection, and clear incident response plans to reduce risks during attacks.
  • Backup and Restore: The provider should offer daily backups, off-site storage, and tested restore options to ensure business continuity.
  • Performance Optimization: Evaluate their caching methods and load testing to support high traffic.
  • Scalability: Your provider should support growth, such as adding subdomains or expanding to multi-site setups.
  • Transparency: Request access to uptime logs, performance metrics, and support documentation to understand what’s being maintained.
  • Technology Compatibility: Ensure the service works with your preferred plugins, tools, and systems.

Affordable Maintenance Solutions for Small Businesses

Small businesses often struggle to strike a balance between costs and reliability. While enterprise-level services offer extensive coverage, many companies don’t need such expensive plans. It’s essential to find providers that deliver affordable packages without sacrificing key security, updates, and backups.

Cost-effective maintenance solutions typically include automated updates, uptime monitoring, malware scanning, regular backups, and basic performance improvements, often at a fraction of the cost of a full-time technical team. These services help businesses stay secure and ensure their site runs smoothly.

The right plan should be easy to manage and reliable, allowing you to focus on attracting customers and growing your business. If a provider offers add-ons, transparent pricing, and straightforward service agreements, it’s likely a good fit.

User Experiences and Feedback on Managed WordPress Maintenance

Many B2B companies find that outsourcing WordPress maintenance reduces their workload and improves website reliability. Regular updates, automated backups, security monitoring, and performance optimization are key benefits.

Professional maintenance helps prevent problems, providing stability during busy times and product launches. Companies with multiple websites, especially those with managed plans, benefit from this, as it reduces plugin conflicts and downtime.

Most users are satisfied but suggest choosing a service with clear deliverables and proactive communication. Overall, businesses appreciate the peace of mind that comes with outsourcing this task.

Common Challenges and How Services Address Them

Here are some of the key challenges that managed WordPress maintenance services can handle.

Frequent Updates and Compatibility Issues

B2B companies often struggle with keeping WordPress up to date, which can lead to compatibility issues if not thoroughly tested. Managed maintenance services test updates in staging environments and apply them only after confirming stability, preventing downtime, and ensuring smooth website functionality.

Growing Security Risks and Vulnerabilities

Security is a significant concern for businesses that use WordPress. Risks like plugin vulnerabilities and malware can disrupt operations. Managed maintenance services offer comprehensive security monitoring, regular scans, robust firewalls, reliable backups, and swift threat responses to maintain a secure environment and minimize downtime and recovery times.

Performance Degradation as Websites Scale

As websites expand, they may become slower, which can impact SEO and user engagement. Maintenance services enhance performance by optimizing caching, cleaning images and databases, configuring CDN, and making hosting adjustments, ensuring the site remains fast and competitive.

Internal Resource Limitations and Time Constraints

Managing WordPress can distract internal teams from essential tasks. Technical issues take time away from campaigns and content creation. Managed maintenance services handle website upkeep, allowing teams to focus on core business activities.

Selecting the Right Maintenance Partner

Choosing a maintenance provider can be a challenging task. Some plans focus solely on basic updates and overlook important areas, such as security and performance. Selecting a service with clear agreements, detailed reporting, and B2B experience ensures effective management and proactive problem-solving.

talk-to-wordpress-expert

Final Verdict: Managed vs DIY WordPress Maintenance

Managed WordPress Maintenance is a strategic investment that protects brand reputation, boosts digital performance, and supports scalability for B2B organizations. As websites become increasingly vital for lead generation and customer experience, reactive management is no longer sufficient.

A dedicated maintenance partner ensures precise execution of updates and optimizations, minimizing the risks of downtime and security breaches. For growth-focused businesses, this leads to consistent performance, enhanced search visibility, and a digital infrastructure that evolves to meet changing business objectives.

7 Proven Strategies to Safeguard Your WordPress eCommerce Store

The global average cost of a data breach in 2024 is $4.88 million—an alarming 10% increase from last year. It’s a staggering number and a wake-up call for all of us in the online retail space.

When customers shop on your site, they expect their personal and payment information to be protected. A security breach can lead to financial losses and, even worse, a loss of trust. And we all know that trust is everything in eCommerce!

A secure online store reassures customers that their sensitive information is safe, fostering loyalty and encouraging repeat business. Here, we’ll explore 7 proven strategies to safeguard your WordPress eCommerce store.

Let’s dive in!

Our 7 Strategies for Your WordPress Store Safety

1. Use HTTPS to Protect Transactions
2. Choose Trusted Payment Processors
3. Opt for Reliable Hosting
4. Strengthen User Account Security
5. Regularly Backup Your Store
6. Monitor User Activity & Access
7. Educate Your Team and Customers

1. Use HTTPS to Protect Transactions

HTTPS (HyperText Transfer Protocol Secure) encrypts data transferred between your website and your customers’ browsers. This encryption makes it much harder for hackers to intercept sensitive information, like credit card details. Displaying HTTPS in the browser’s address bar signals to customers that their data is secure. A padlock icon reassures users that the site is trustworthy, which can significantly reduce cart abandonment rates and increase conversion rates.

Moreover, search engines like Google prioritize HTTPS websites in their rankings. By adopting HTTPS, eCommerce stores can improve their visibility in search results, potentially driving more traffic and sales.

Many payment processors and regulatory bodies require HTTPS for online transactions. Using HTTPS helps ensure compliance with standards such as PCI DSS (Payment Card Industry Data Security Standard), which is essential for accepting credit card payments.

How we implement:
  • Get an SSL Certificate: Purchase an SSL certificate from your hosting provider or a trusted certificate authority. Many hosts offer free options, like Let’s Encrypt.
  • Install the Certificate: Follow your host’s instructions to install the SSL certificate. Most providers have a simple setup process.
  • Redirect HTTP to HTTPS: Ensure that all traffic is redirected to the secure version of your site. This can usually be done in your website’s settings or via your .htaccess file.

Security for WooCommerce plugin ensures SSL is configured correctly and assists with PCI-DSS compliance for handling payment information.

2. Choose Trusted Payment Processors

Customers are more likely to complete purchases when they see familiar and reputable payment options. Well-known processors like PayPal, Stripe, and Square carry a reputation for security, which helps build trust and can lead to higher conversion rates.

Many established payment processors offer user-friendly interfaces and seamless integration with WordPress. This enhances the overall shopping experience, making it easier for customers to complete transactions and reducing cart abandonment rates.

Reputable payment processors typically support multiple currencies and various payment methods, including credit cards, digital wallets, and bank transfers. This flexibility can cater to a broader audience and enhance the store’s global reach.

What to look for:
  • Security Certifications: Ensure the processor complies with PCI-DSS (Payment Card Industry Data Security Standard), which sets security requirements for handling credit card information.
  • User Reviews: Check reviews for customer feedback on reliability and security.

WordFence Security plugin monitors traffic and provides login security features such as two-factor authentication (2FA).

3. Opt for Reliable Hosting

Fast-loading websites are crucial for eCommerce success. Reliable hosts utilize high-performance servers and Content Delivery Networks (CDNs) to optimize site speed. A well-performing site improves user experience, reduces bounce rates, and increases conversion rates.

Reliable hosting providers implement robust security measures, such as firewalls, DDoS protection, and malware scanning. These features help protect the eCommerce store from various cyber threats, including hacking attempts and data breaches.

As your eCommerce business grows, your hosting needs may change. Reliable hosting services offer scalable solutions that allow you to upgrade your resources (such as bandwidth and storage) easily, ensuring your site can handle increased traffic without compromising performance.

Key Features to Consider:
  • Automatic Updates: Ensure your host automatically updates WordPress core, themes, and plugins.
  • Backups: Choose a host that provides regular backups, so you can restore your site easily if something goes wrong.

Sucuri Security plugin helps mitigate the risks of DDoS attacks and malware infections.

4. Strengthen User Account Security

User accounts typically store sensitive information such as names, addresses, and payment methods. By enhancing account security, you significantly reduce the risk of unauthorized access and data breaches.

When customers feel their accounts are secure, they are more likely to make purchases and return to your store. Building trust through security measures can lead to increased customer loyalty and sales.

Strong account security measures help prevent unauthorized transactions and account takeovers. This not only protects the business but also fosters trust with customers.

Tips for Implementation:

  • Use plugins like Google Authenticator or Wordfence to set up 2FA for both admin and customer accounts.
  • Provide easy instructions for customers on how to enable 2FA.

2FA adds an extra layer of security by requiring a second form of verification (like a text message) in addition to a password.

5. Regularly Backup Your Store

Regular backups protect against data loss due to hacks or technical failures. If something goes wrong, you want to be able to restore your site quickly.

Analyzing user activity can provide insights into potential vulnerabilities in your security protocols. This information can guide improvements, allowing you to adapt your security measures based on real user behavior.

Our Easy Backup Solutions:

Keep track of failed login attempts and set thresholds for account lockouts. Notifying users of failed attempts can prompt them to strengthen their passwords or enable additional security measures.
Use user-friendly plugins like UpdraftPlus or BackupBuddy to automate backups. Set your backups to run daily or weekly, depending on how often you update your site.

Aim for daily backups if you frequently add new products or content. For less active sites, weekly backups may suffice.

6. Monitor User Activity and Access

Early detection allows for prompt action to mitigate potential threats. Regularly monitoring user activity can help identify unusual patterns, such as repeated failed login attempts or access from unfamiliar IP addresses.

Account takeovers are a significant threat in eCommerce. Monitoring user activities can help detect signs of account compromise, such as unexpected changes to user profiles or unauthorized transactions. Swift intervention can mitigate damage and protect both customer data and business assets.

Understanding how users interact with your site can provide valuable insights into their preferences and behaviors. This information can help you optimize the user experience while identifying potential security weaknesses based on usage patterns.

Easy Implementation Tips:
  • IP Address Monitoring: Track the IP addresses from which users log in. Identify and flag logins from unusual or unexpected locations, allowing for additional verification steps if necessary.
  • Regularly Review Activity Logs: Schedule routine audits of user activity logs to identify any patterns or anomalies. This proactive monitoring can help catch potential security issues before they escalate.

Jetpack Security offers a complete suite of features including real-time backups, malware scanning, and spam protection.

7. Educate Your Team and Customers

Many security breaches occur due to human error, such as weak passwords or falling for phishing scams. Training your team to recognize these risks helps minimize mistakes that could compromise the store’s security.

Many data protection regulations require businesses to implement training programs for employees regarding data security and privacy. Educating your team helps ensure compliance and protects your business from legal repercussions.

Regularly educating your team about security is one best practice. This can be done by recognizing phishing emails and using secure connections.

Easy Ways for Informing Customers:
  • Customer Awareness Campaigns: Implement campaigns to educate customers about account security. This could include blog posts, email newsletters, and social media content that highlight best practices for online safety.
  • Phishing Awareness: Provide training and resources that help users recognize phishing attempts. This includes identifying suspicious emails and messages that could lead to compromised accounts.

Send out security tips through newsletters or blog posts to keep security awareness high among your customer base.

End Note

A secure eCommerce store is not just a necessity; it’s a promise to your customers that their shopping experience will be safe and trustworthy. By focusing on creating a secure shopping experience, you’re not just protecting your business; you’re also fostering confidence and loyalty among your customers. Every time they make a purchase, they should feel safe and supported, knowing that you’re taking every possible step to safeguard their data.

By implementing robust security measures, you demonstrate to your customers that their safety is your top priority. Ultimately, the commitment to security transforms your eCommerce store into a trusted space for customers to explore and shop. A secure shopping environment not only enhances the customer experience but also serves as a powerful differentiator in a crowded marketplace.

Investing in the security of your WordPress eCommerce store is an investment in your business’s future. Connect with us to elevate your eCommerce store security standards. We secure your storefront with our customized security measures for eCommerce store owners.

WordPress 6.3 Unwrapped: Discover What’s New and Exciting

WordPress 6.3 marks the second major release of 2023, bringing with it a plethora of notable updates, fresh features, enhancements, and bug fixes that amplify the strength and utility of WordPress. With the changes that are spread across 43 core components, WordPress 6.3 opens new possibilities for the creative expression of designers, creators, and builders.

Within this post, we’ll unveil the highlights of WordPress 6.3 and spotlight the features that deserve your attention following the update.

Let’s take a look!

Enhancements in Selectors API

Designed to elevate your styling capabilities to unprecedented heights, this advanced API empowers you with the ability to configure multiple CSS selectors, ensuring a seamless generation of global styles across your blocks. Notably, this can be achieved across three distinct levels: root, feature, and sub-feature.

  • Root Selectors At the core of the Selectors API lies the root selector, your block’s principal CSS selector. Every block requires a primary CSS selector to orchestrate global style declarations. Should you not designate one through the Block Selectors API, rest assured that a default selector (in the form of .wp-block-) will be generated for you.
  • Feature-level Selectors In the new version, API empowers you to target specific block features with unparalleled precision – be it borders, colors, typography, or other attributes. This facet enables you to bestow distinct styles upon various elements within your block. For instance, imagine applying color schemes to your block’s wrapper while refining typographic elements within an inner text element.
  • Subfeature Selectors The Subfeature Selectors elevate your styling prowess to unparalleled heights. Now, individual styles associated with block features (e.g., background-color or border-radius) can be expressed through unique selectors. This proves invaluable when aiming to implement diverse styles within a single feature. Consider a scenario where the block’s typography necessitates font family at the wrapper level while specifying distinct text decoration and font size for inner elements.

The brand-new Command Palette

This exciting feature takes center stage within the post and site editors, granting users swift access through keyboard shortcuts, namely ctrl + k or command + k. It offers two avenues to maximize command utilization: static and dynamic commands.

  • Static Commands: Easily register static commands using the wp.data.dispatch( wp.commands.store ).registerCommand action or the wp.commands.useCommand React hook. With either approach, a command object is provided, equipped with a distinct name, a clear label, an icon, a callback function invoked upon command selection, and potentially, a context.
  • Dynamic Commands: Dynamic commands, on the other hand, are enabled via “command loaders.” These prove invaluable when command availability hinges on user-input search terms or certain conditions.
you design img

The command palette’s versatility extends to contextual commands, ensuring priority visibility and a seamless user experience. These commands shine in specific contexts, such as navigating the site editor or editing a template. Currently, two key contexts have been implemented:

  • Site-editor – While navigating the site editor with the sidebar visible.
  • Site-editor-edit – When engaged in editing a document (template, template part, or page) within the site editor.
  • And the journey doesn’t end here. As adoption grows, additional contexts will be seamlessly incorporated

To manipulate the command palette’s behavior, it is enriched with a host of selectors and actions through the WordPress Data API. These include:

  • Retrieving registered commands and command loaders with selectors like getCommands and getCommandLoader.
  • Checking whether the command palette is open via the isOpen selector.
  • Programmatic control over opening and closing the command palette using the open and close actions.

Evolution of Layout Support

The latest WordPress 6.3 update brings exciting enhancements to layout support, marking its graduation from experimental to stable. While the functionality remains consistent, the upgrade comes with a small change: when you’re adding block support for layout in your block.json, the syntax “layout” now replaces “__experimentalLayout.” Although the support for the “__experimentalLayout” syntax will still be retained for a transitional period, we strongly recommend that you seize the opportunity to elevate your custom blocks by transitioning to the rock-solid layout syntax.

Innovations in CSS Specificity for Enhanced Layouts:

When you offer something valuable in exchange for someone’s email (like a free trial, eBook, or exclusive demo), you’re not just collecting random email addresses. You’re attracting leads who are genuinely interested in what your software can do. This means the leads you gather are more likely to convert into paying clients.

Empowering Complex Block Markup with Classnames:
9. WordPress 62

Building on the foundation laid in WordPress 6.2, the latest version integrated layout classnames into the block inner wrapper. While this aligns with the outer wrapper for most blocks, certain blocks (like the core Cover block) encompass multiple inner containers. With WordPress 6.3, a novel classname graces the inner wrapper of all blocks with layout, amalgamating the block classname with the layout classname.

Say Hello to the New Grid Layout:

Embrace innovation with the introduction of the all-new grid layout type, underpinned by the power of CSS Grid. This dynamic layout defaults to an auto-fill approach, complete with configurable column widths. For those seeking precise control, the columnCount property within the layout object allows you to establish a fixed number of columns.

Elevated Layout and Spacing in the Post Template Block:

Embrace innovation with the introduction of the all-new grid layout type, underpinned by the power of CSS Grid. This dynamic layout defaults to an auto-fill approach, complete with configurable column widths. For those seeking precise control, the columnCount property within the layout object allows you to establish a fixed number of columns.

Seamless Spacer Block Alignment with Parent Layouts:
9. WordPress 6

Spacer blocks now seamlessly integrate with parent layout configurations, taking on the orientation of the parent layout, especially within flex-type layout blocks. While you can still manually set an orientation for Spacer blocks based on parent context, flex layouts grant priority to the flex orientation, ensuring consistent and harmonious designs.

Dynamic Coloring of Social Icons Block

The Social Icons block now offers the option to customize both the “Icon color” and “Icon background color” in WordPress 6.3. Prior to this version, the chosen colors were hardcoded as hex code values within the block, even if you selected a color from the theme palette defined in theme.json.

Now, with WordPress 6.3 release, the Social Icons block embraces CSS classes that seamlessly align with your chosen color values. These classes are an integral part of the WordPress ecosystem, ingeniously generated in harmony with the color palette outlined in your theme.json file. Their structure is straightforward:

has-[color_slug]-color

has-[color_slug]-background-color

It’s essential to note that these empowering classes won’t come into play when a user opts for a custom color. This dynamic integration ensures that your design retains its integrity and aligns seamlessly with your chosen color palette, making WordPress 6.3 the pinnacle of design control and cohesion.

Bundled Themes Drops Internet Explorer Scripts and Styles

In recognition of the diminishing traffic from Internet Explorer users and WordPress’ discontinuation of support for this outdated browser, certain default themes have taken proactive steps. By removing specific Internet Explorer-oriented scripts and styles, these themes are ensuring that the majority of users can enjoy a smoother and faster browsing journey.

Moreover, these optimizations extend to focus enhancement scripts that were previously tailored for Internet Explorer and older versions of Chrome. With the arrival of WordPress 6.3, themes like Twenty Thirteen and Twenty Fourteen have gracefully evolved, no longer incorporating these scripts in their functions.js files. Additionally, from Twenty Fifteen to Twenty Twenty-One, themes have been fine-tuned to neither enqueue nor print these scripts.

This strategic move not only aligns with modern web standards but also reflects our commitment to delivering a top-tier experience for every user. Embrace these enhancements as we usher in a new era of optimized performance and a richer online encounter.

Improvements to the Cache API

WordPress 6.3 release brings forth an array of strategic enhancements that redefine how queries are cached within the WordPress ecosystem.

Elevating Cache Group Dynamics:

Diving into the heart of WordPress 6.3, a paradigm shift in cache group dynamics emerges. Previous versions of WordPress stored query results in cache groups aligned with their corresponding objects. However, the landscape has evolved, and WordPress 6.3 introduces a groundbreaking approach that offers developers unprecedented control and precision.

As the WP_User_Query class joins the cache hierarchy, a dynamic modification unfolds. The introduction of distinct cache groups tailored for queries becomes the cornerstone of this evolution. Developers now hold the reins to specify cache group expiration times, enabling the fine-tuning of cache duration. The innovative wp_cache_flush_group() function stands ready for developers seeking tailored cache clearance.

Flexibility extends even further, granting developers the ability to designate cache groups as non-persistent, if necessary. The newly introduced cache groups encompass:

  • post-queries
  • term-queries
  • comment-queries
  • network-queries (global cache group)
  • site-queries (global cache group)
  • user-queries (global cache group)

Enhancement to get_pages() Function

WordPress 6.3 introduces a significant improvement to the get_pages()function. It now utilizes WP_Query internally, addressing a 13-year-old ticket (#12821). This update reduces complexity by offloading database queries and cache handling to WP_Query.

As a result, this eliminates redundancy and ensures that all filters within WP_Query apply to get_pages(). Users employing filters like posts_pre_query or posts_results for customized WP_Query behavior, including data retrieval from alternative sources such as cache or other databases, will benefit. Additionally, a new filter named get_pages_query_args has been added, allowing developers to modify parameters passed to WP_Query while maintaining compatibility with original arguments.

PHP Support

WordPress 6.3 no longer provides support for PHP 5.

The minimum supported PHP version has been raised to 7.0.0.

Wrap Up

WordPress 6.3 release represents a significant leap in the editing experience. The improvements are substantial, covering various new editing features in the site editor, a redesigned and versatile block pattern system, new blocks, improved performance, enhanced accessibility, and internationalization enhancements, among other improvements.

If you’re thinking about upgrading your WordPress site to leverage these remarkable advancements, our skilled team of WordPress professionals is here to offer seamless assistance and guidance. Embrace the capabilities of WordPress 6.3 and discover new possibilities for your online presence.

WordPress 6.3 introduces notable improvements aimed at enhancing load time performance for content containing images. The impact of these enhancements is particularly evident in the Largest Contentful Paint (LCP) metric, which gauges the time taken from the request initiation until the largest content element within the viewport is rendered.

Automated fetchpriority Support

WordPress 6.3 latest release, now includes the fetchpriority attribute, set to “high,” within the image tag it identifies as the “LCP image” – the image constituting the largest content within the viewport. This attribute instructs the browser to prioritize this image, boosting LCP performance by approximately 5-10%. For further context, refer to the initial proposal post.

Automated lazy-loading

A series of refinements and resolutions have been introduced to enhance the automatic management of lazy-loading using the loading attribute. This refinement process, initiated in WordPress 5.9 and continued in 6.2, culminates in comprehensive enhancements in WordPress 6.3. This meticulous approach ensures the more accurate identification of images where omission of the attribute is appropriate, thereby contributing to optimized performance. For deeper insights into the significance of not lazy-loading in-viewport images, especially the LCP image, in the context of performance, refer to the relevant WordPress 5.9 dev note post.